
1
 →
control-theory/gonzo is an open-source project on GitHub, mainly written in Go. Gonzo! The Go based TUI log analysis tool It currently holds 2,769 stars and 111 forks with 0 open issues, and was last pushed on an unknown date (repository created unknown).
AI Homed tracks it on the Local & On-Device AI board.
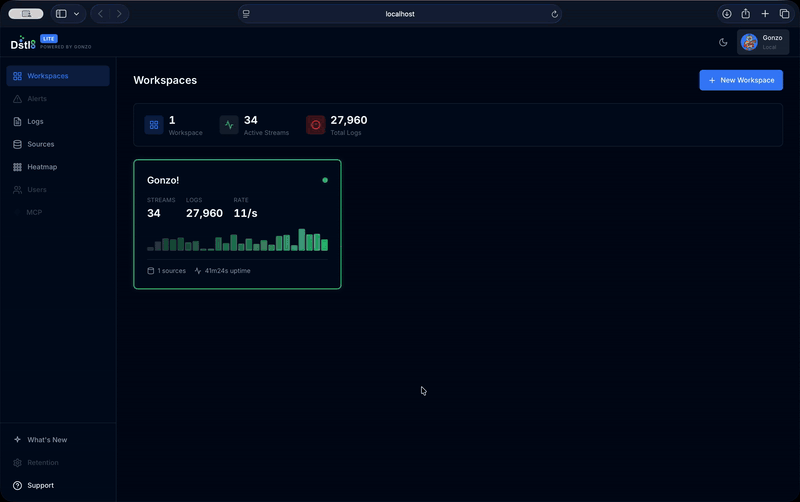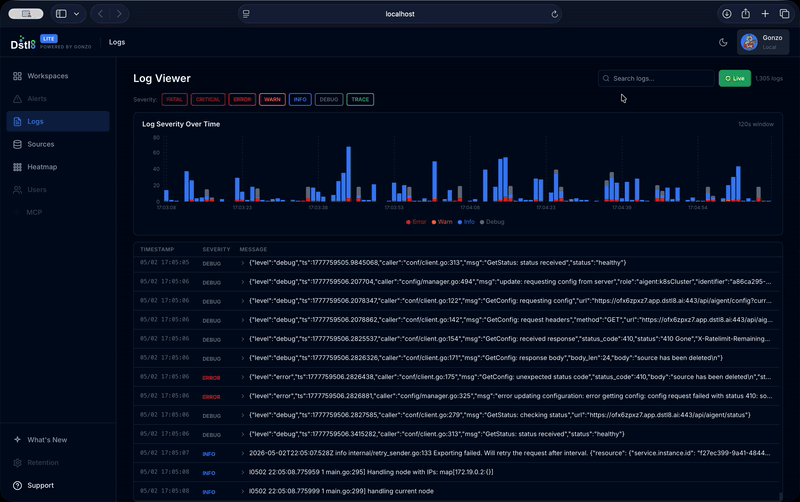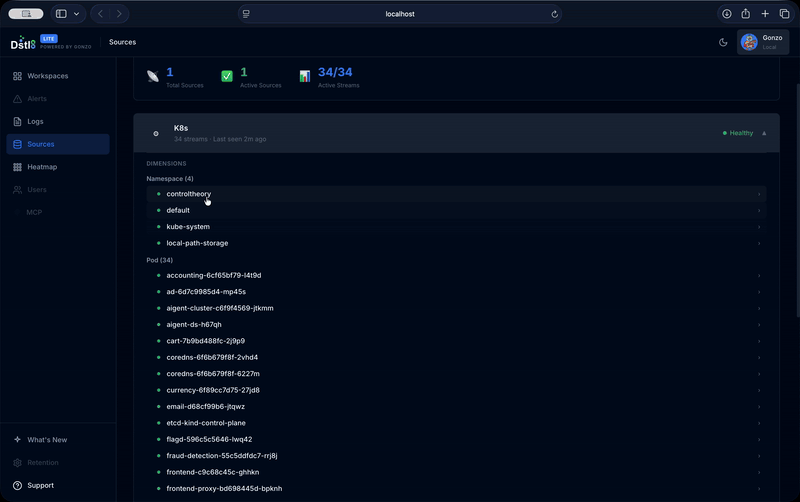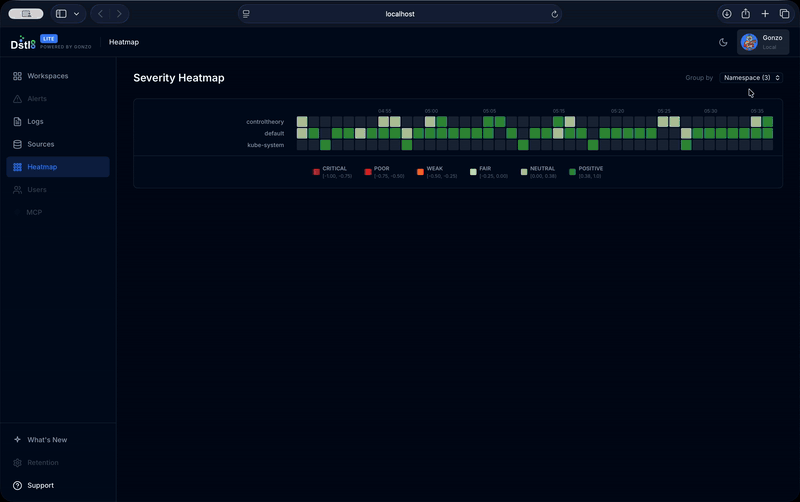
🆕 NEW: Press d from any Gonzo view to launch Dstl8.Lite ↓ - a local browser-based dashboard with workspaces, log search, and severity heatmaps.


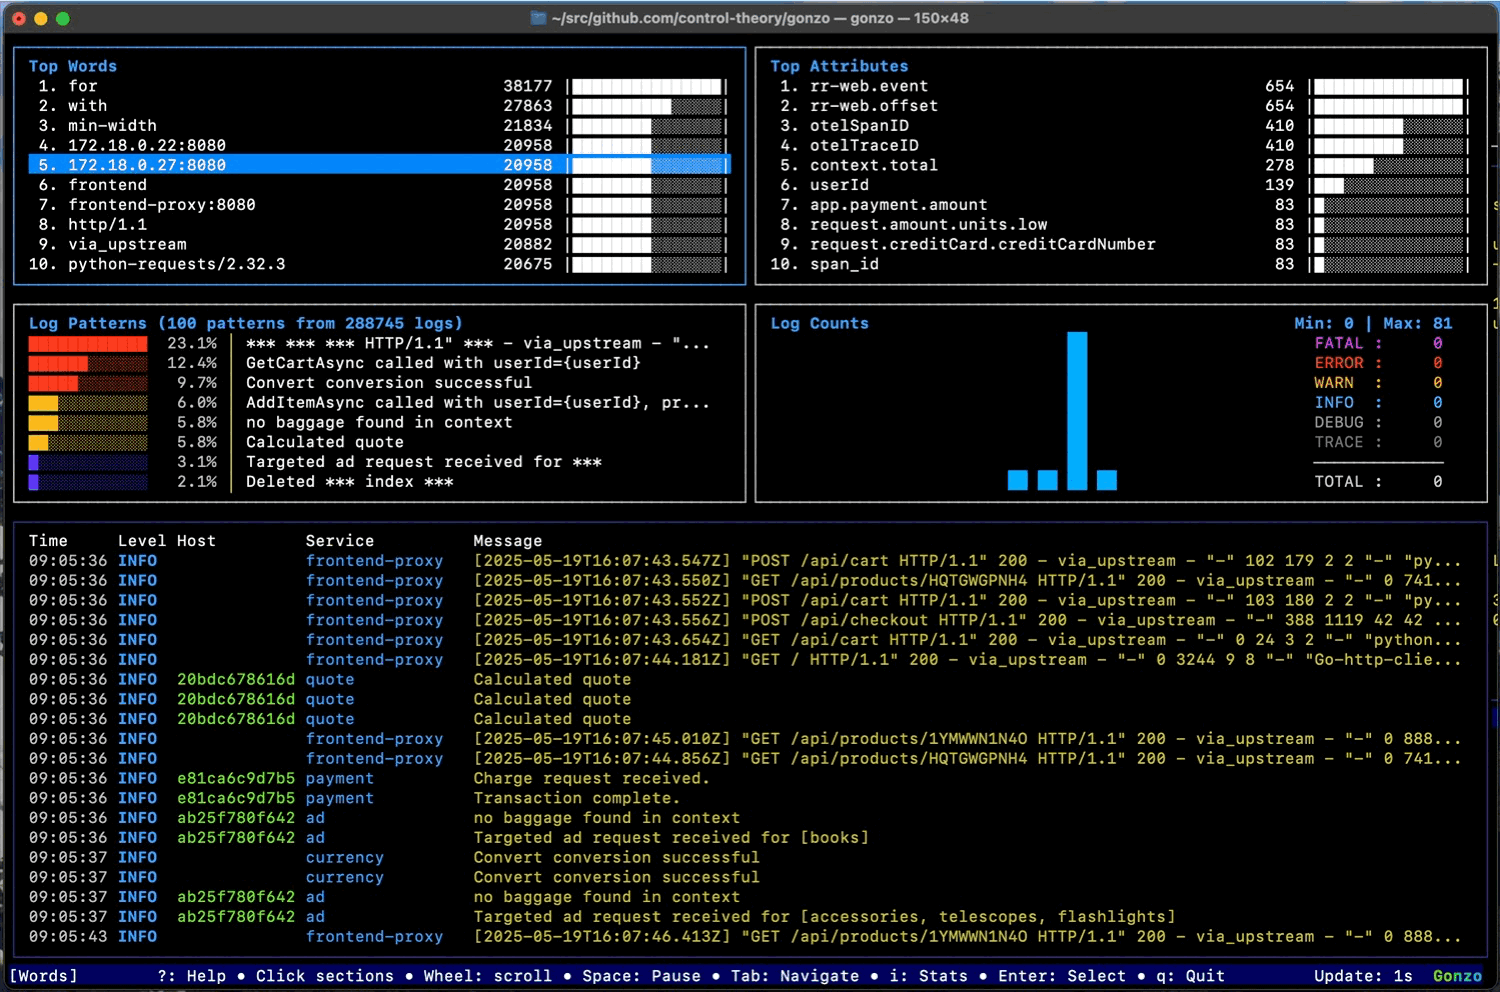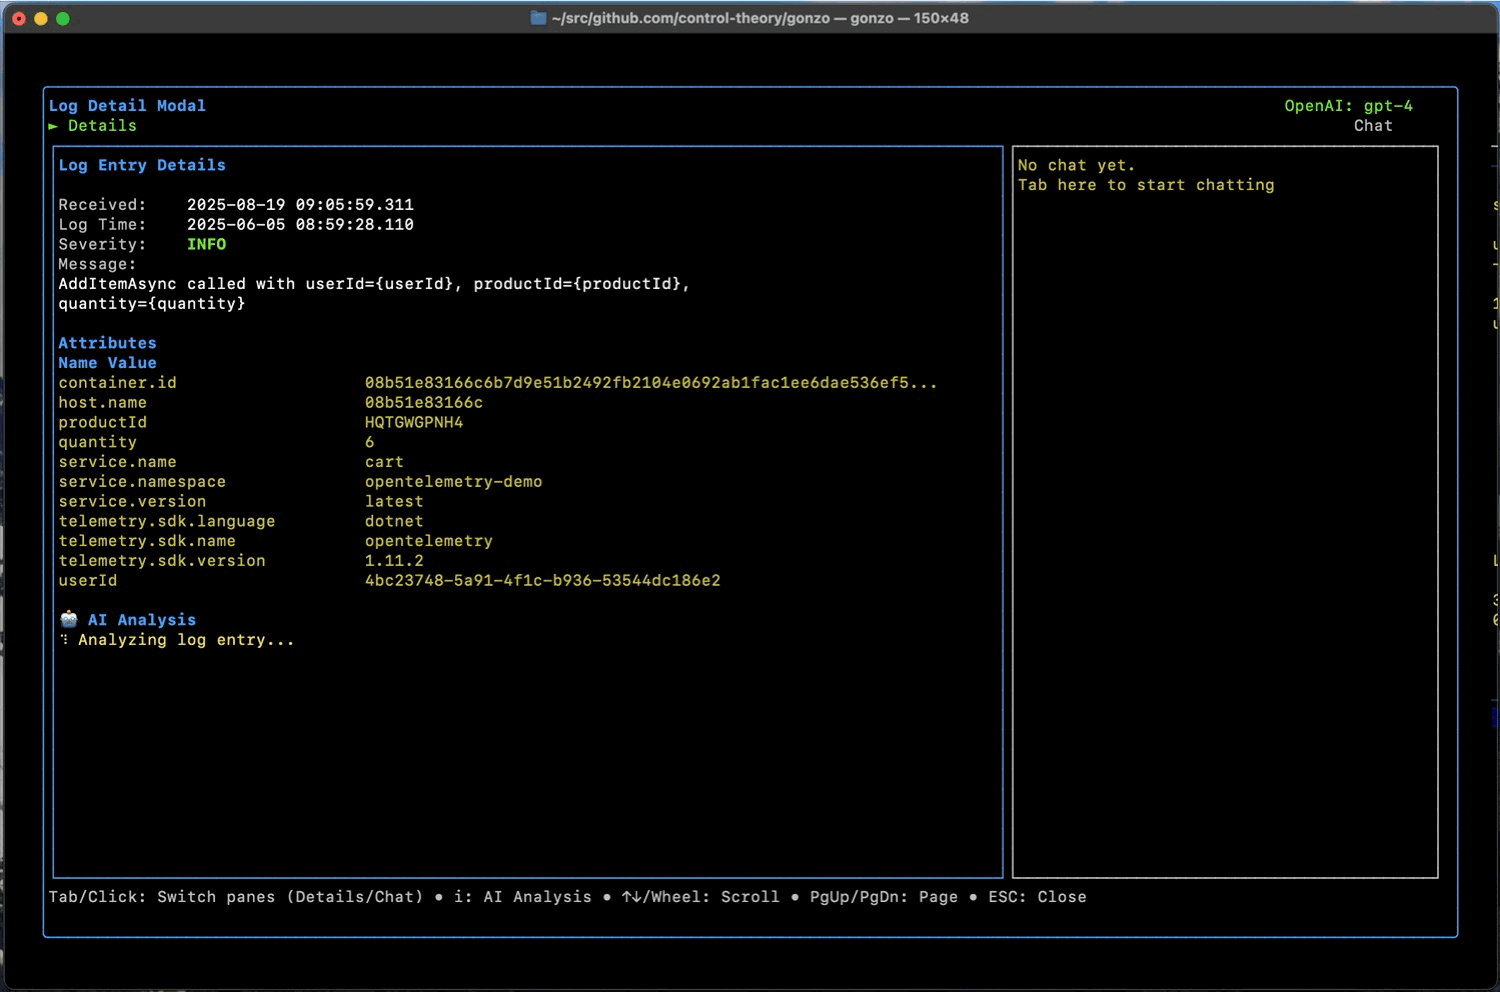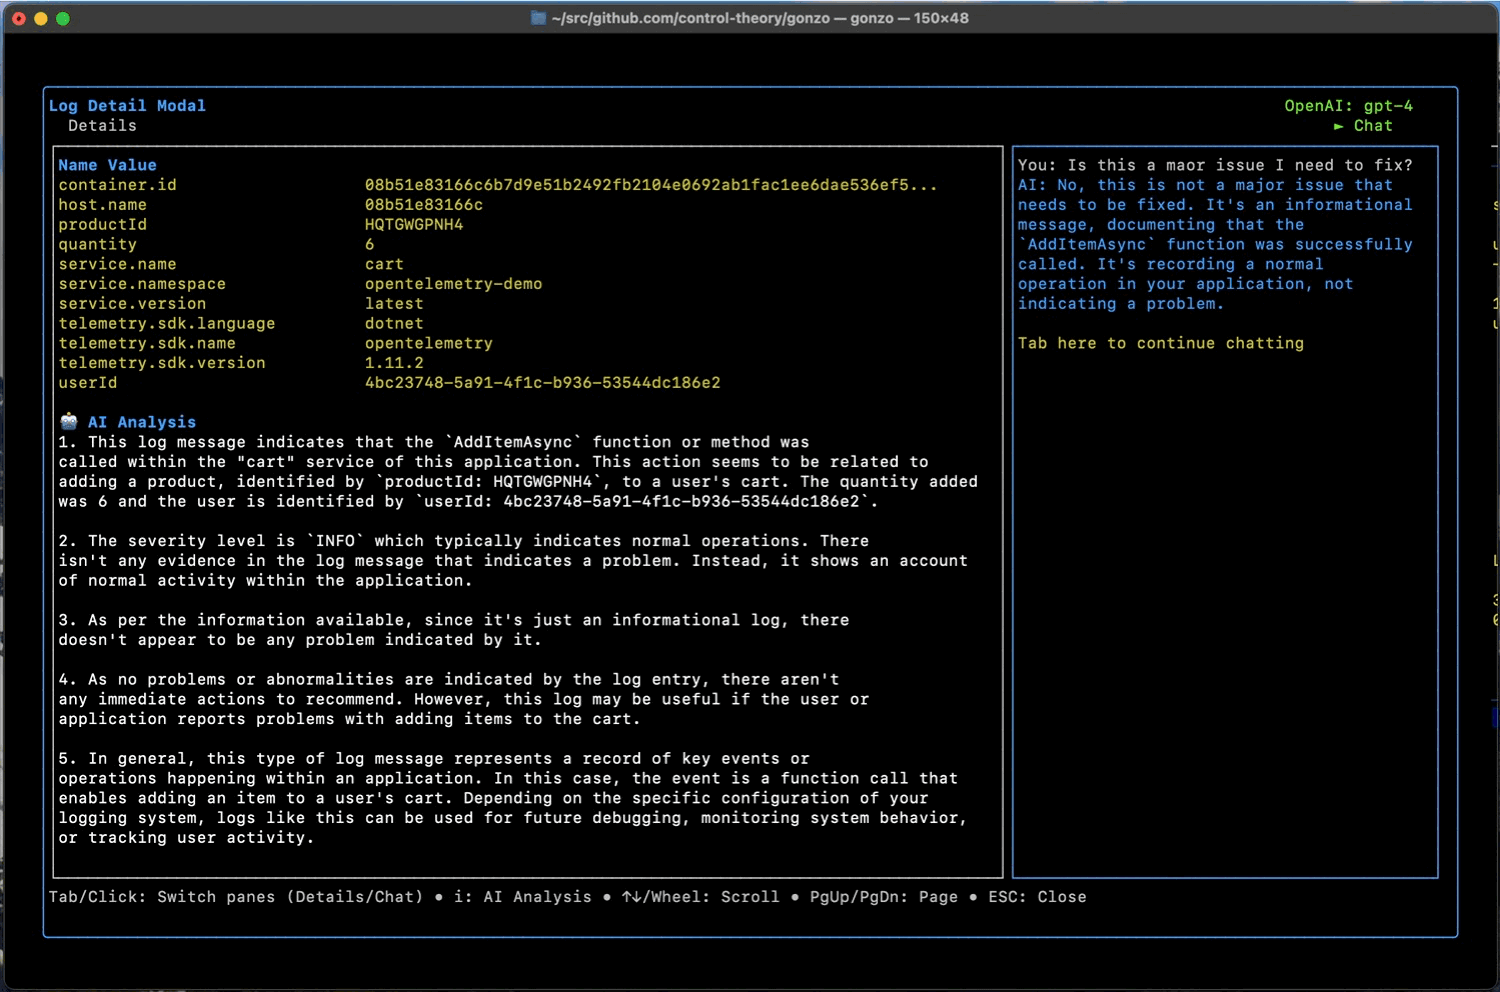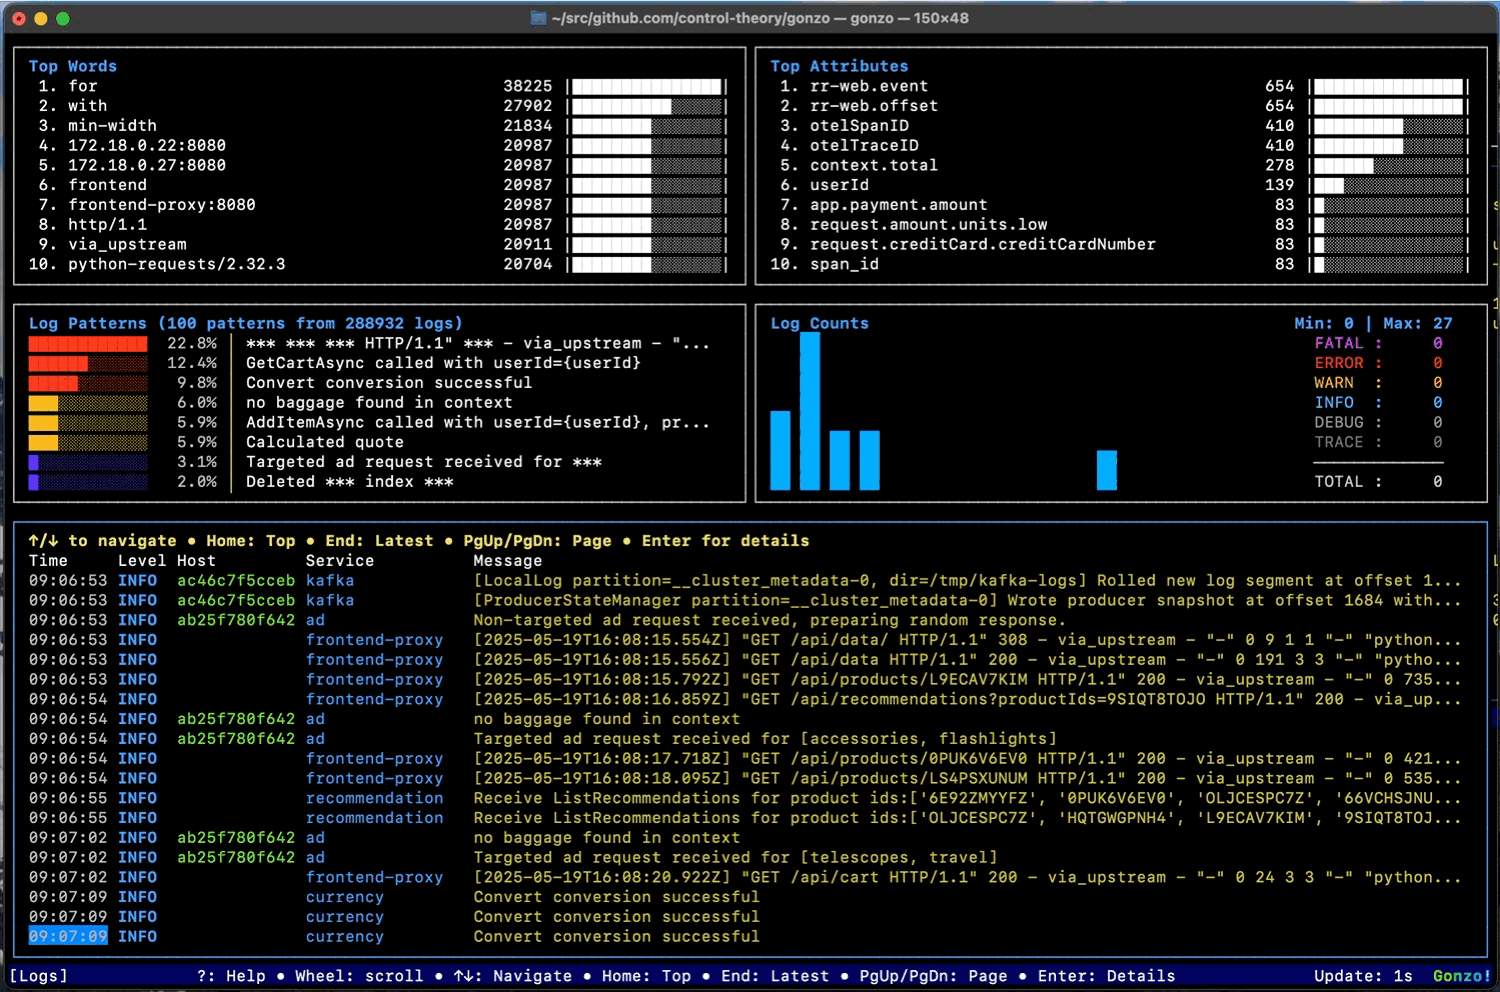
A powerful, real-time log analysis terminal UI inspired by k9s. Analyze log streams with beautiful charts, AI-powered insights, and advanced filtering.
Here are some references to get you started:
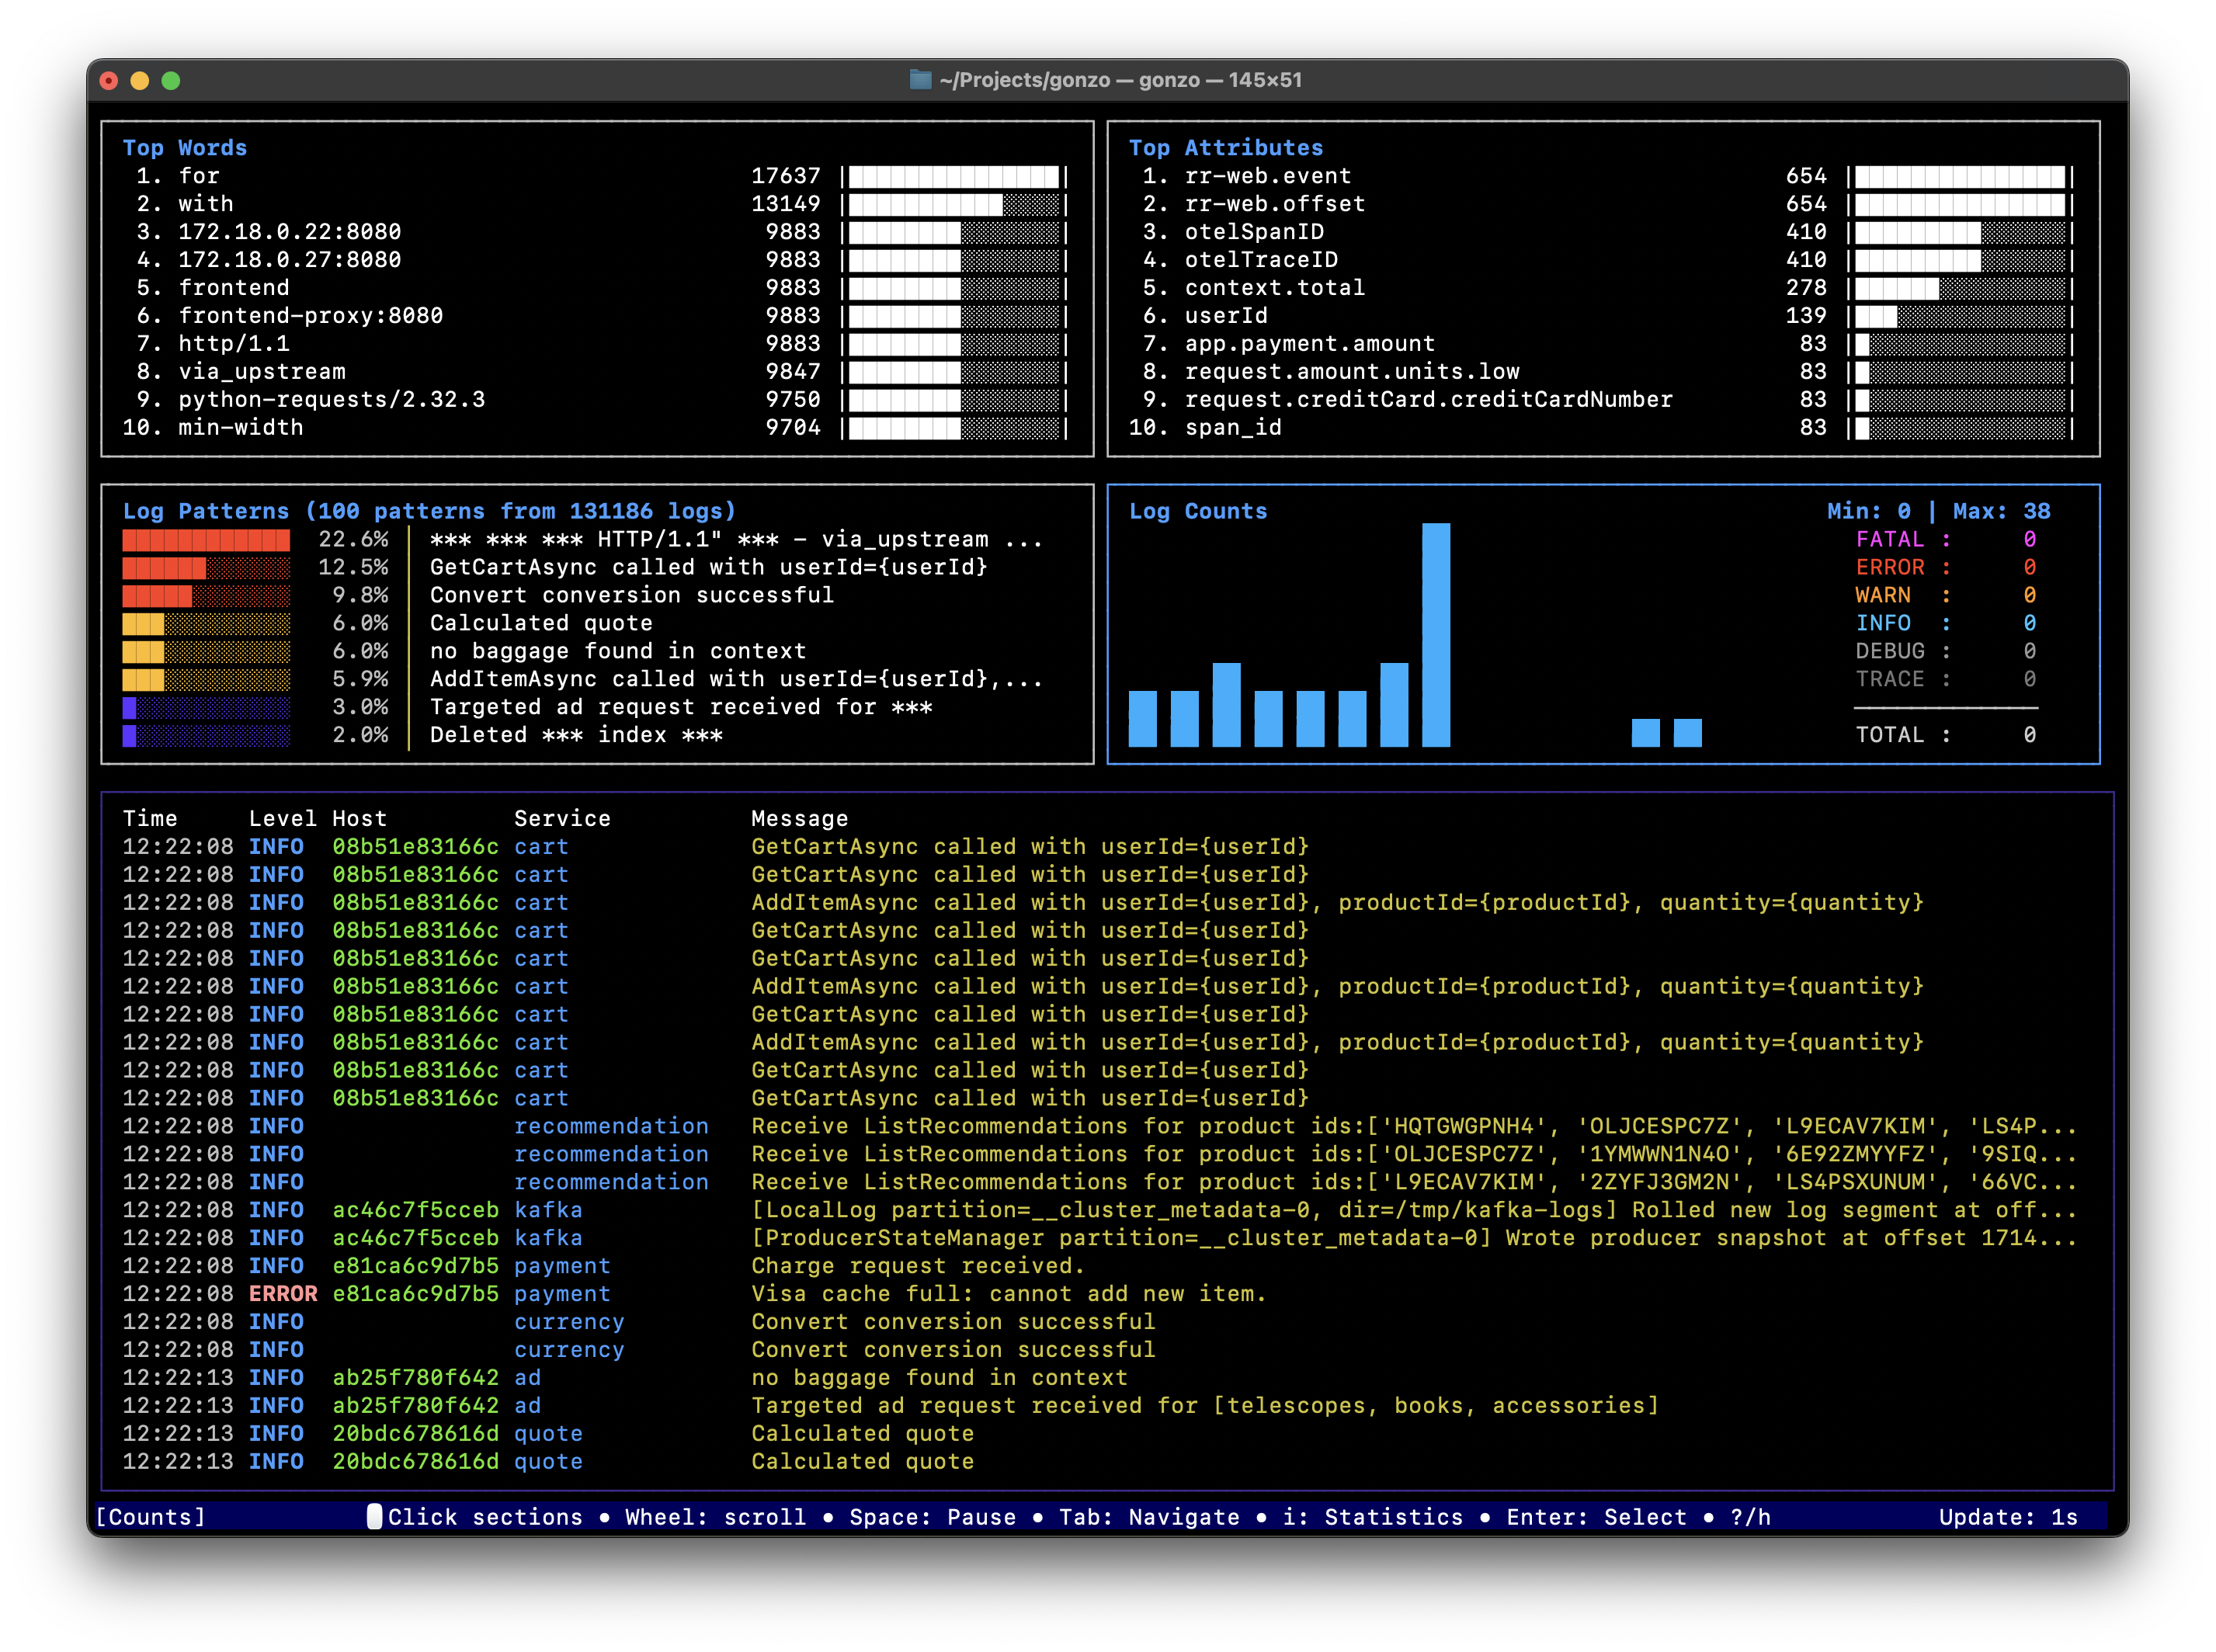
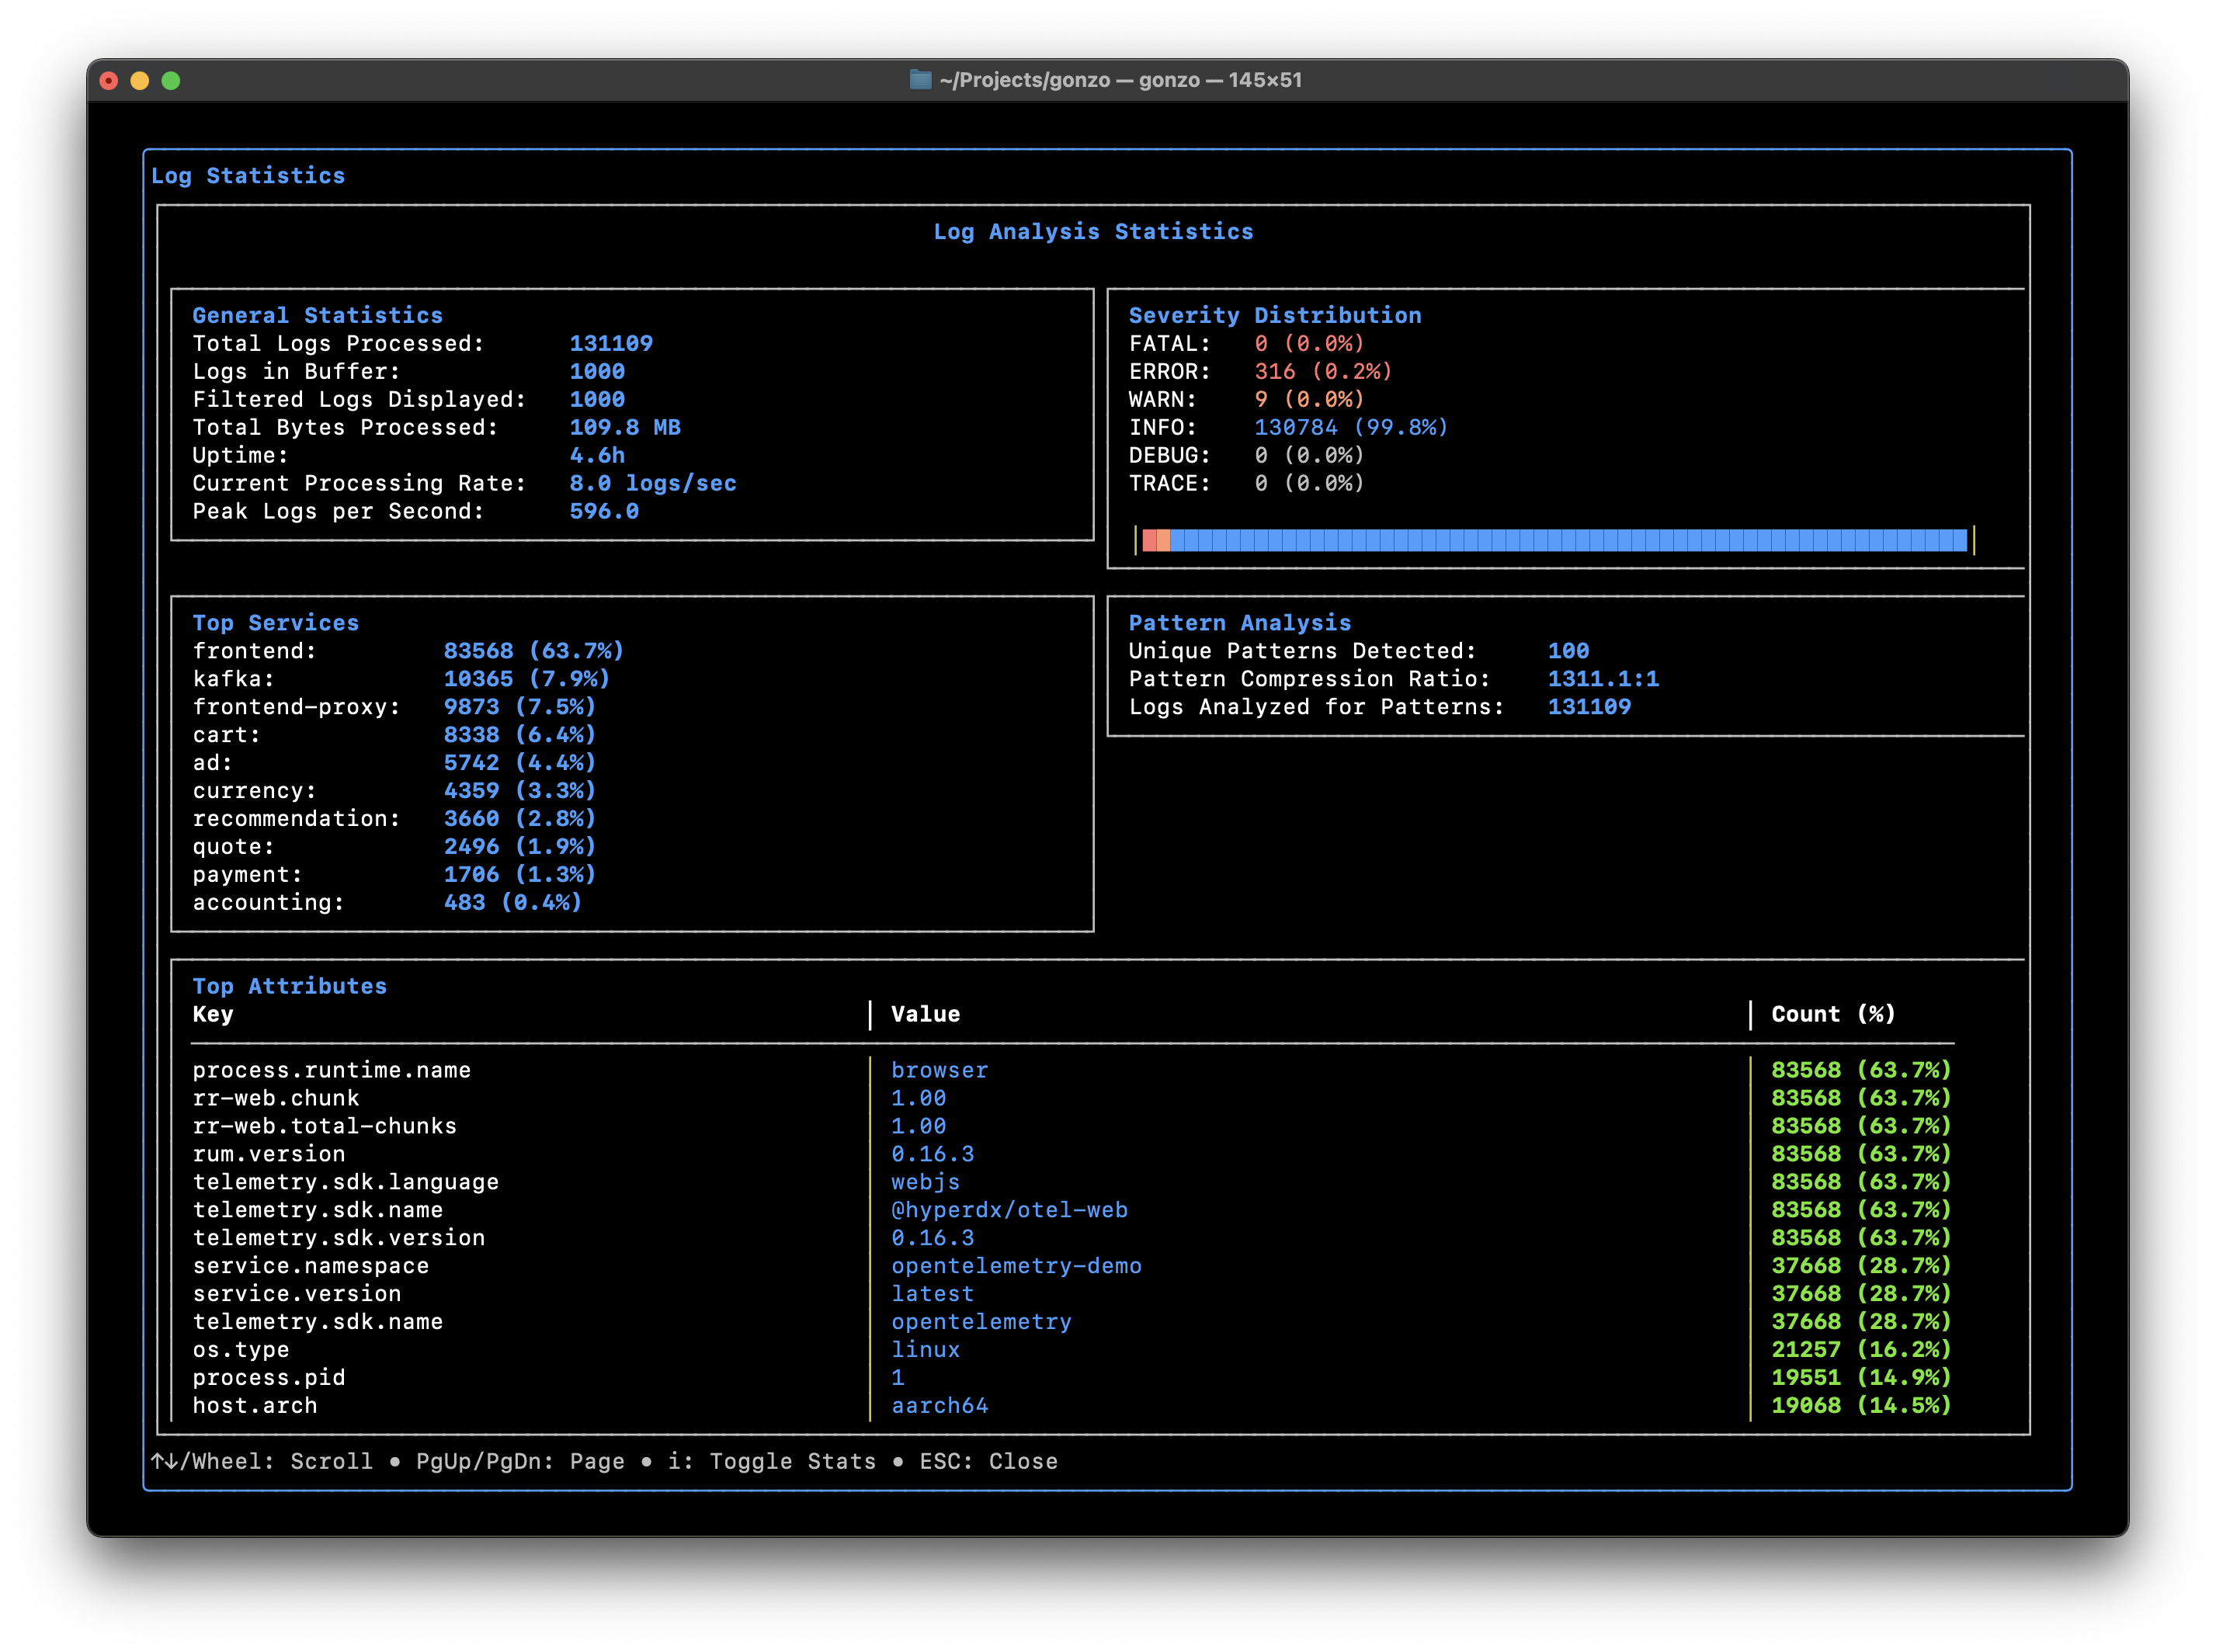
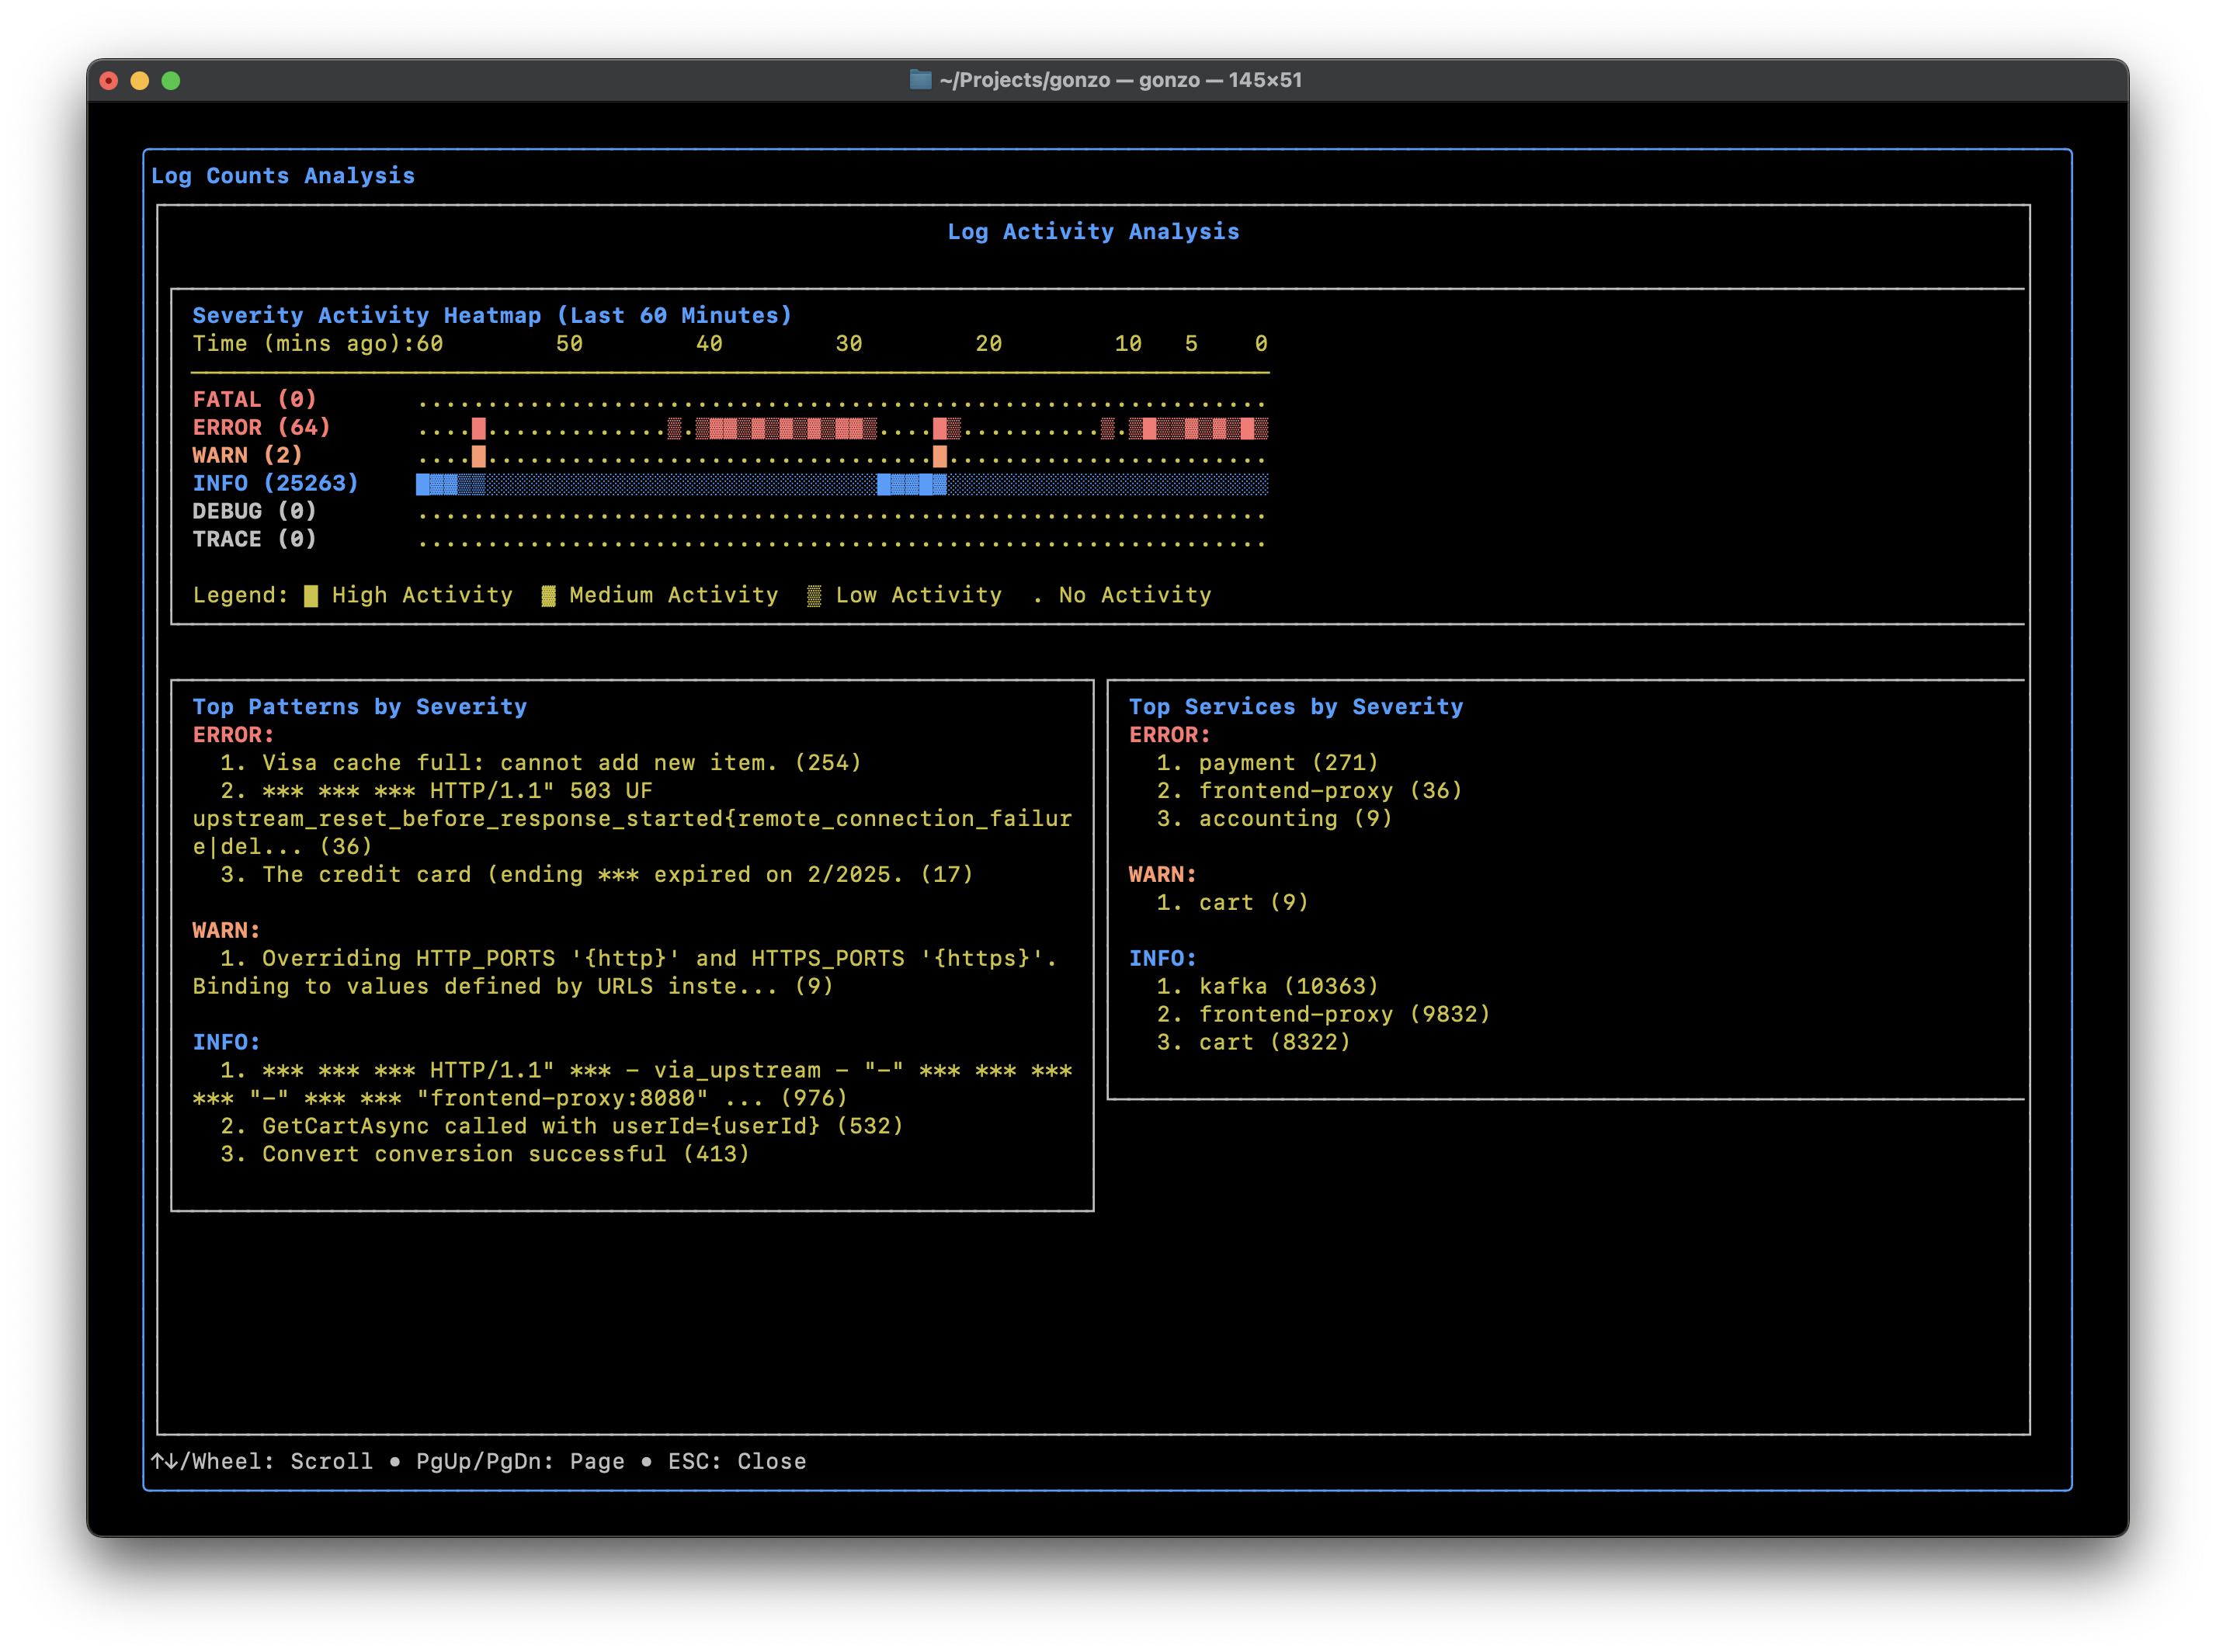
d for Dstl8.LiteHit d from any Gonzo view to launch Dstl8.Lite - a local GUI that streams the same logs Gonzo is analyzing into a richer, browser-based dashboard with workspaces, pattern detection, severity heatmaps, and live log search. All running locally and powered by Gonzo under the hood.
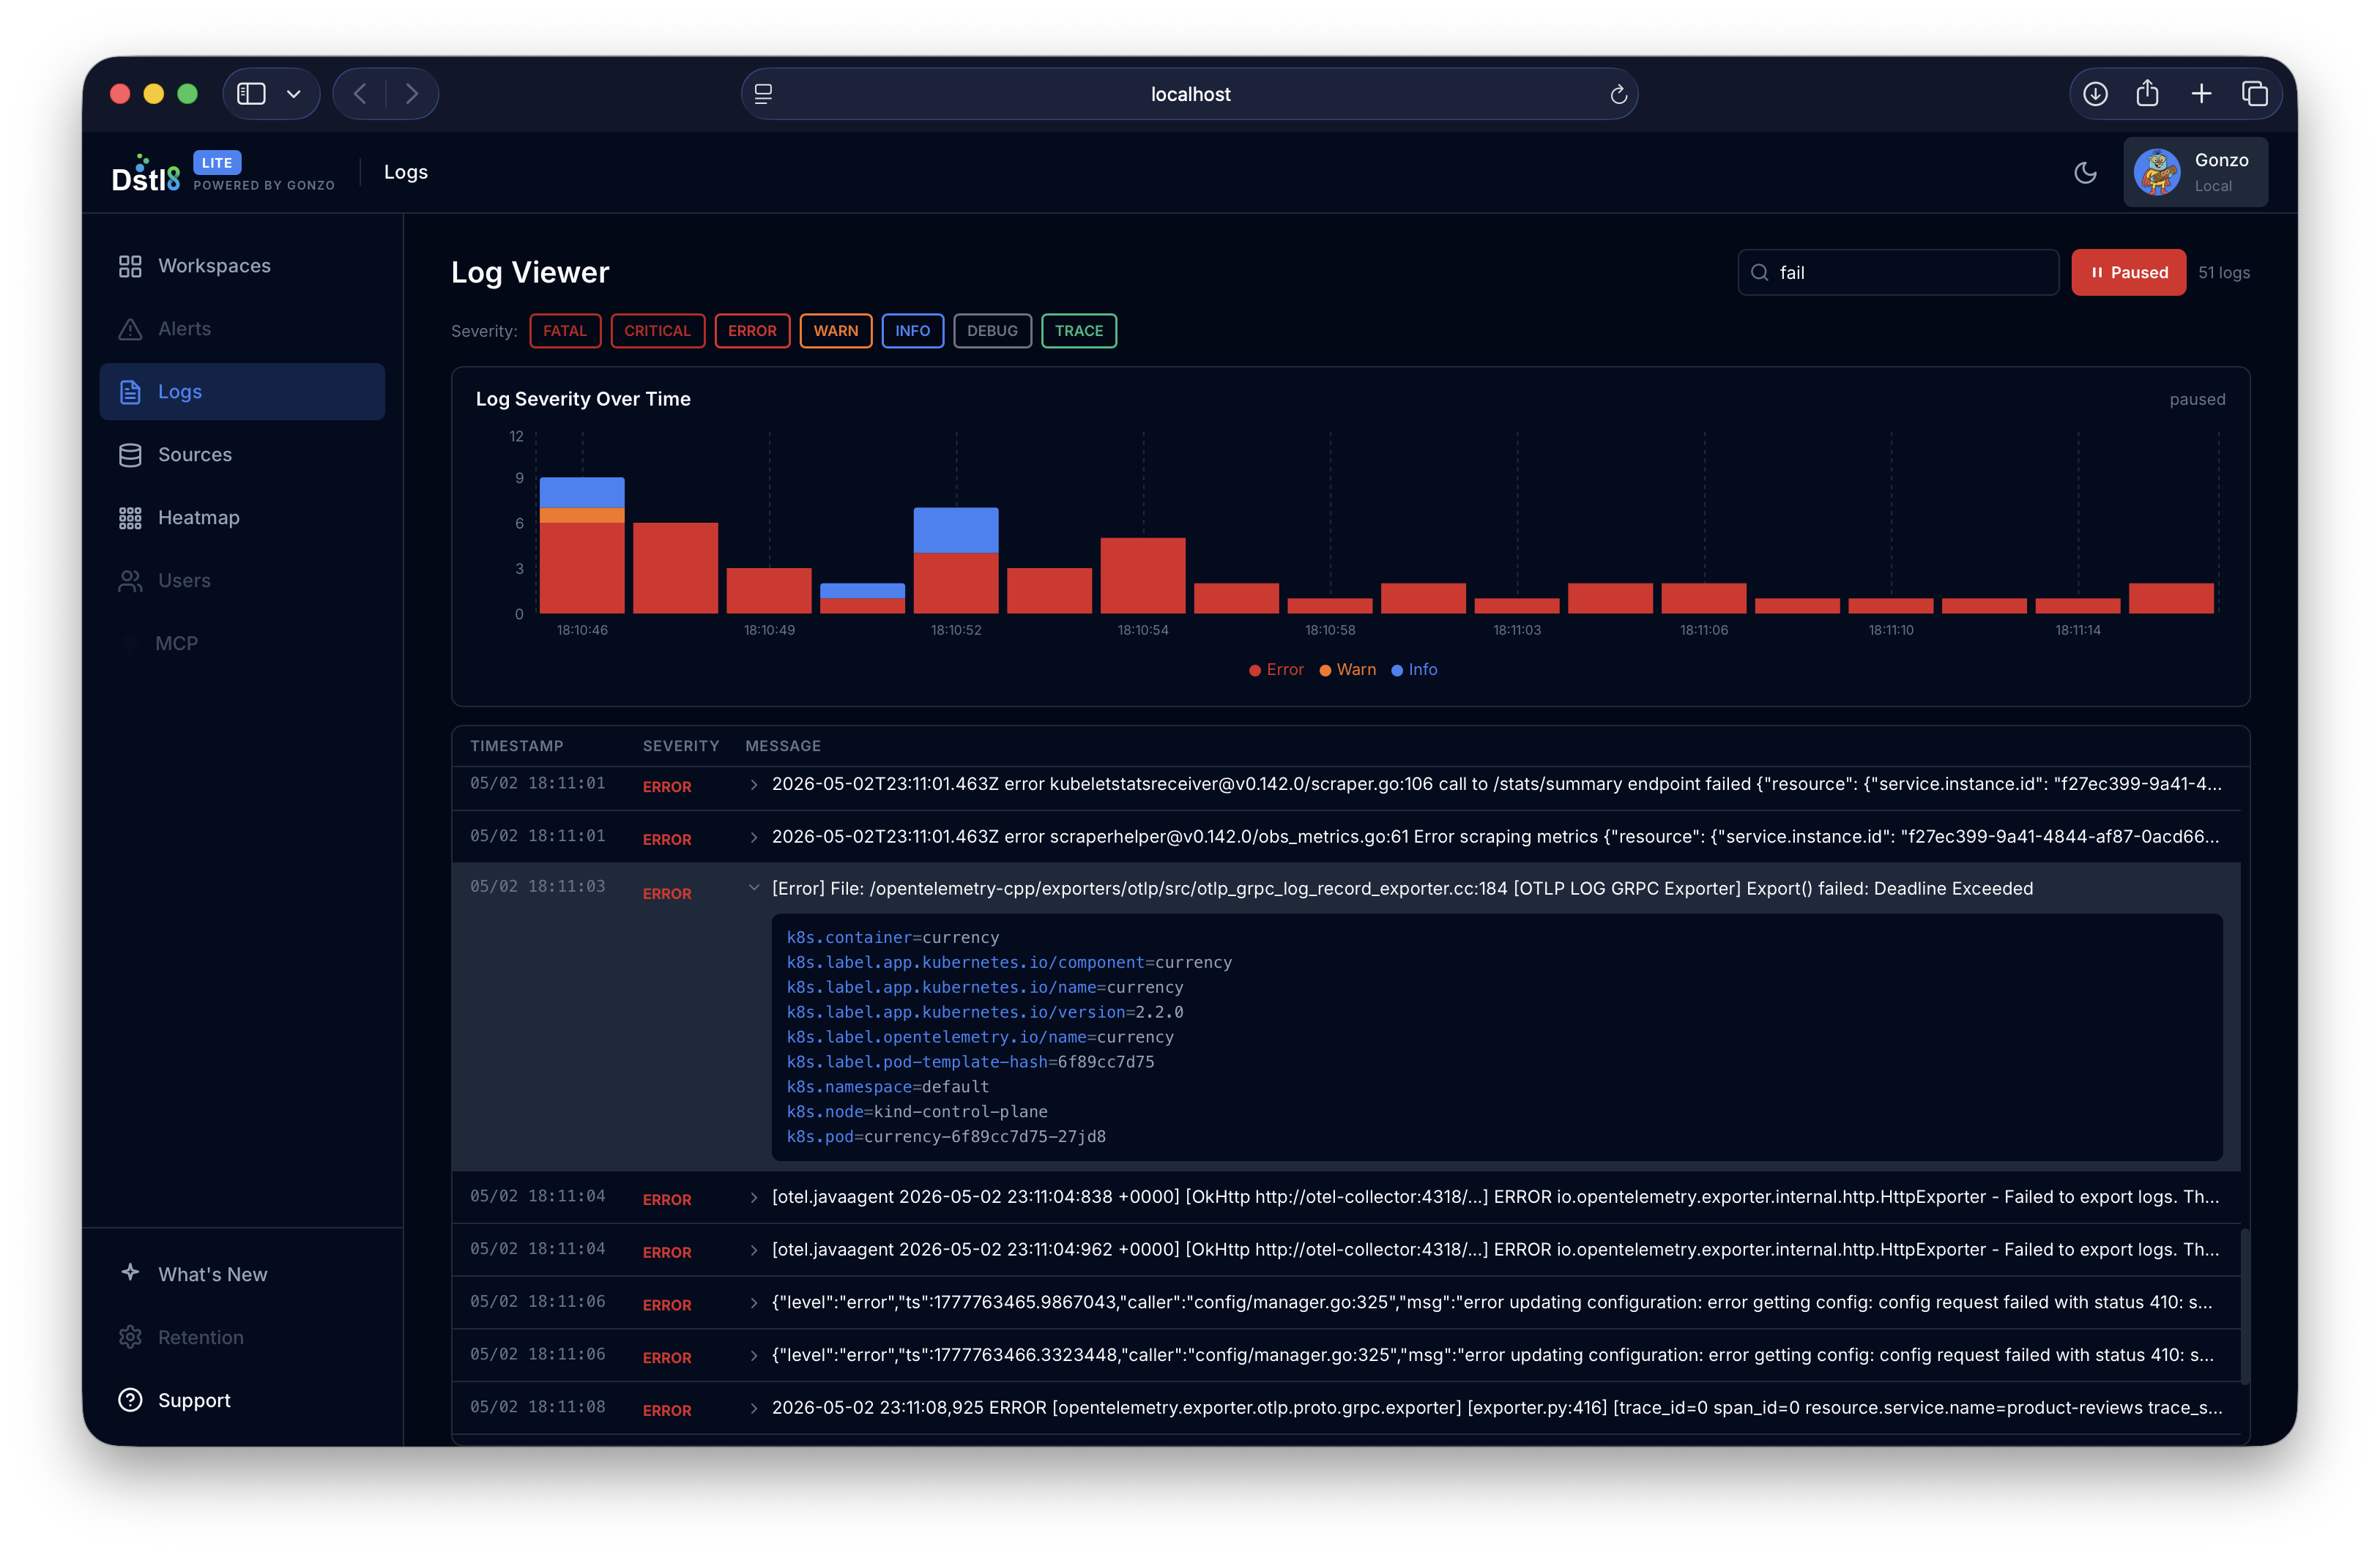
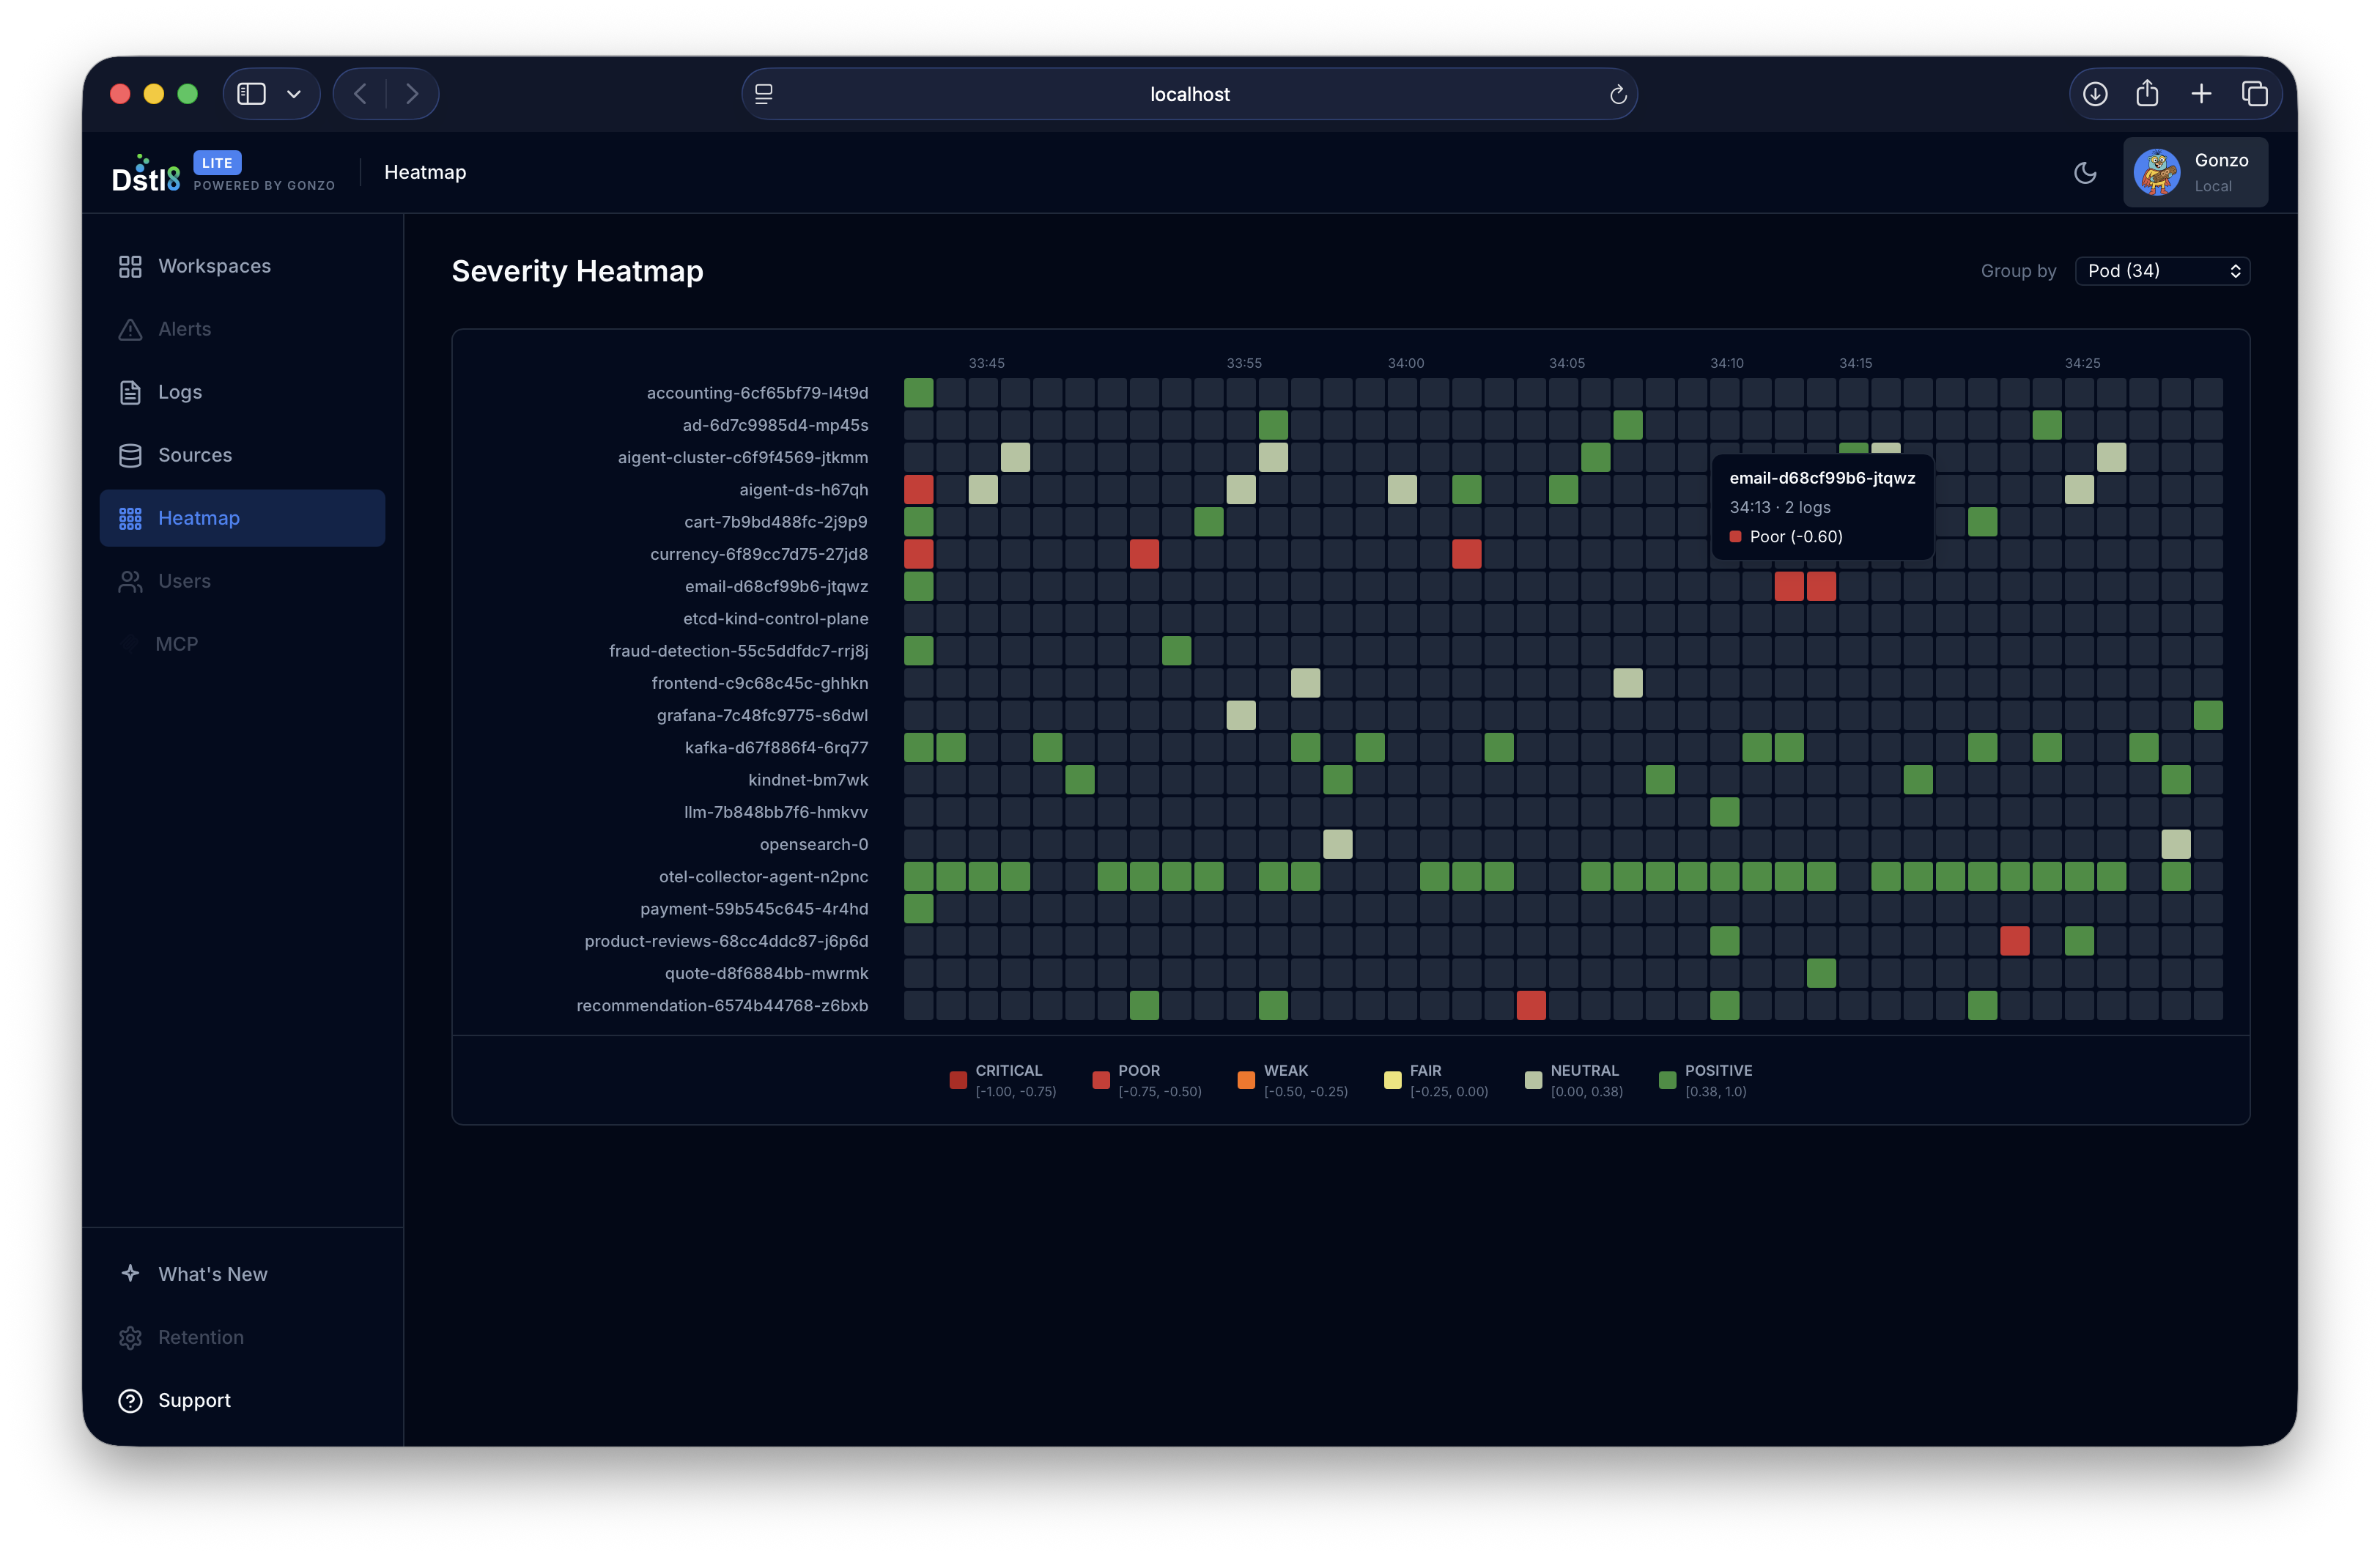
f to open a dedicated fullscreen modal for log browsing with all navigation featuresgo install github.com/control-theory/gonzo/cmd/gonzo@latest
brew install gonzo
Download the latest release for your platform from the releases page.
nix run github:control-theory/gonzo
git clone https://github.com/control-theory/gonzo.git
cd gonzo
make build
This repo includes a Claude Code plugin with a guided log-analysis skill. Inside Claude Code:
/plugin marketplace add control-theory/gonzo
/plugin install gonzo@gonzo
Then ask Claude to "tail my logs", "watch my Vercel logs", or "analyze my Kubernetes logs". The skill detects your deployment platform, installs Gonzo if needed, configures AI analysis, and generates the right pipe command with platform-specific normalizers. See skills/gonzo/ for the skill content.
# Read logs directly from files
gonzo -f application.log
Read from multiple files
gonzo -f application.log -f error.log -f debug.log
Use glob patterns to read multiple files
gonzo -f "/var/log/*.log"
gonzo -f "/var/log/app/.log" -f "/var/log/nginx/.log"
Follow log files in real-time (like tail -f)
gonzo -f /var/log/app.log --follow
gonzo -f "/var/log/*.log" --follow
Analyze logs from stdin (traditional way)
cat application.log | gonzo
Stream logs directly from Kubernetes clusters
gonzo --k8s-enabled=true --k8s-namespaces=default
gonzo --k8s-enabled=true --k8s-namespaces=production --k8s-namespaces=staging
gonzo --k8s-enabled=true --k8s-selector="app=my-app"
Stream logs from kubectl (traditional way)
kubectl logs -f deployment/my-app | gonzo
Follow system logs
tail -f /var/log/syslog | gonzo
Analyze Docker container logs
docker logs -f my-container 2>&1 | gonzo
With AI analysis (requires API key)
export OPENAI_API_KEY=sk-your-key-here
gonzo -f application.log --ai-model="gpt-4"
Press d once Gonzo is running to launch the Dstl8.Lite GUI in your browser
Gonzo supports custom log formats through YAML configuration files. This allows you to parse any structured log format without modifying the source code.
Some example custom formats are included in the repo, simply download, copy, or modify as you like! In order for the commands below to work, you must first download them and put them in the Gonzo config directory.
# Use a built-in custom format
gonzo --format=loki-stream -f loki_logs.json
List available custom formats
ls ~/.config/gonzo/formats/
Use your own custom format
gonzo --format=my-custom-format -f custom_logs.txt
Custom formats support:
Gonzo can receive logs directly via OpenTelemetry Protocol (OTLP) over both gRPC and HTTP:
# Start Gonzo as an OTLP receiver (both gRPC on port 4317 and HTTP on port 4318)
gonzo --otlp-enabled
Use custom ports
gonzo --otlp-enabled --otlp-grpc-port=5317 --otlp-http-port=5318
gRPC endpoint: localhost:4317
HTTP endpoint: http://localhost:4318/v1/logs
Using gRPC:
exporters:
  otlp/gonzo_grpc:
    endpoint: localhost:4317
    tls:
      insecure: true
service:
  pipelines:
    logs:
      receivers: [your_receivers]
      processors: [your_processors]
      exporters: [otlp/gonzo_grpc]
Using HTTP:
exporters:
  otlphttp/gonzo_http:
    endpoint: http://localhost:4318/v1/logs
service:
  pipelines:
    logs:
      receivers: [your_receivers]
      processors: [your_processors]
      exporters: [otlphttp/gonzo_http]
Using gRPC:
from opentelemetry.exporter.otlp.proto.grpc._log_exporter import OTLPLogExporter
exporter = OTLPLogExporter(
    endpoint="localhost:4317",
    insecure=True
)
Using HTTP:
from opentelemetry.exporter.otlp.proto.http._log_exporter import OTLPLogExporter
exporter = OTLPLogExporter(
    endpoint="http://localhost:4318/v1/logs",
)
See examples/send_otlp_logs.py for a complete example.
# Auto-select best available model (recommended) - file input
export OPENAI_API_KEY=sk-your-key-here
gonzo -f logs.json
Or specify a particular model - file input
export OPENAI_API_KEY=sk-your-key-here
gonzo -f logs.json --ai-model="gpt-4"
Follow logs with AI analysis
export OPENAI_API_KEY=sk-your-key-here
gonzo -f "/var/log/app.log" --follow --ai-model="gpt-4"
Using local LM Studio (auto-selects first available)
export OPENAI_API_KEY="local-key"
export OPENAI_API_BASE="http://localhost:1234/v1"
gonzo -f logs.json
Using Ollama (auto-selects best model like gpt-oss:20b)
export OPENAI_API_KEY="ollama"
export OPENAI_API_BASE="http://localhost:11434"
gonzo -f logs.json --follow
Using Claude Code (uses sonnet by default)
gonzo --ai-provider=claude-code -f logs.json
Claude Code with specific model
gonzo --ai-provider=claude-code --ai-model=haiku -f /var/log/app.log --follow
Traditional stdin approach still works
export OPENAI_API_KEY=sk-your-key-here
cat logs.json | gonzo --ai-model="gpt-4"
Gonzo includes an embedded web dashboard that runs alongside the TUI. It starts automatically on port 5718.
# Gonzo starts the web dashboard automatically
gonzo -f application.log --follow
Open http://localhost:5718 in your browser
Use a custom port
gonzo -f application.log --web-port=3000
Disable the web dashboard
gonzo -f application.log --web-disabled
The dashboard includes:
| Key/Mouse | Action |
| ------------------- | -------------------------------------------------------- |
| Tab / Shift+Tab | Navigate between panels |
| Mouse Click | Click on any section to switch to it |
| ↑/↓ or k/j | Move selection up/down |
| Mouse Wheel | Scroll up/down to navigate selections |
| ←/→ or h/l | Horizontal navigation |
| Enter | View log details or open analysis modal (Counts section) |
| ESC | Close modal/cancel |
| Key | Action |
| -------------- | ----------------------------------------- |
| Space | Pause/unpause entire dashboard |
| / | Enter filter mode (regex supported) |
| s | Search and highlight text in logs |
| d | Launch Dstl8.Lite GUI in browser |
| Ctrl+f | Open severity filter modal |
| Ctrl+k | Open Kubernetes filter modal (k8s mode) |
| f | Open fullscreen log viewer modal |
| c | Toggle columns (Host/Service ↔ Namespace/Pod in k8s mode) |
| C | Configure visible columns (column picker) |
| r | Reset all data (manual reset) |
| u / U | Cycle update intervals (forward/backward) |
| i | AI analysis (in detail view) |
| m | Switch AI model (shows available models) |
| ? / h | Show help |
| q / Ctrl+C | Quit |
| Key | Action |
| ------------------ | --------------------------------------------- |
| Home | Jump to top of log buffer (stops auto-scroll) |
| End | Jump to latest logs (resumes auto-scroll) |
| PgUp / PgDn | Navigate by pages (10 entries at a time) |
| ↑/↓ or k/j | Navigate entries with smart auto-scroll |
| Key | Action |
| ----- | ---------------------------------------- |
| c | Start chat with AI about current log |
| Tab | Switch between log details and chat pane |
| m | Switch AI model (works in modal too) |
The severity filter modal (Ctrl+f) provides fine-grained control over which log levels to display:
| Key | Action |
| ------------------ | ------------------------------------------------- |
| ↑/↓ or k/j | Navigate severity options |
| Space | Toggle selected severity level on/off |
| Enter | Apply filter and close modal (or select All/None) |
| ESC | Cancel changes and close modal |
Features:
The column picker modal (C key) lets you configure which columns are visible in the log viewer:
| Key | Action |
| ------------------ | ----------------------------------- |
| ↑/↓ or k/j | Navigate column options |
| Space | Toggle selected column on/off |
| Enter | Apply changes and close modal |
| ESC | Discard changes and close modal |
Features:
(N/M active) indicating how many columns are currently enabledPress Enter on the Counts section to open a comprehensive analysis modal featuring:
gonzo [flags]
gonzo [command]
Commands:
  version     Print version information
  help        Help about any command
  completion  Generate shell autocompletion
Flags:
  -f, --file stringArray           Files or file globs to read logs from (can specify multiple)
  --follow                         Follow log files like 'tail -f' (watch for new lines in real-time)
  --format string                  Log format to use (auto-detect if not specified). Can be: otlp, json, text, or a custom format name
  -u, --update-interval duration   Dashboard update interval (default: 1s)
  -b, --log-buffer int             Maximum log entries to keep (default: 1000)
  -m, --memory-size int            Maximum frequency entries (default: 10000)
  --ai-provider string             AI provider to use: 'openai' (default), 'claude-code'
  --ai-model string                AI model for analysis (auto-selects best available if not specified)
  -s, --skin string                Color scheme/skin to use (default, or name of a skin file)
  --stop-words strings             Additional stop words to filter out from analysis (adds to built-in list)
Web Dashboard Flags:
  --web-port int                   Port for the Dstl8 Lite web dashboard (default: 5718)
  --web-disabled                   Disable the web dashboard
Kubernetes Flags:
  --k8s-enabled=true               Enable Kubernetes log streaming mode
  --k8s-namespaces stringArray      Kubernetes namespace(s) to watch (can specify multiple, default: all)
  --k8s-selector string            Kubernetes label selector for filtering pods
  --k8s-tail int                   Number of previous log lines to retrieve (default: 10)
  --k8s-since int                  Only return logs newer than relative duration in seconds
  --k8s-kubeconfig string          Path to kubeconfig file (default: $KUBECONFIG or $HOME/.kube/config)
  --k8s-context string             Kubernetes context to use
-t, --test-mode                  Run without TTY for testing
  -v, --version                    Print version information
  --config string                  Config file (default: $HOME/.config/gonzo/config.yml)
  -h, --help                       Show help message
Create ~/.config/gonzo/config.yml for persistent settings:
# File input configuration
files:
- "/var/log/app.log"
- "/var/log/error.log"
- "/var/log/*.log" # Glob patterns supported
follow: true # Enable follow mode (like tail -f)
Update frequency for dashboard refresh
update-interval: 2s
Buffer sizes
log-buffer: 2000
memory-size: 15000
UI customization
skin: dracula # Choose from: default, dracula, nord, monokai, github-light, etc.
Additional stop words to filter from analysis
stop-words:
- "log"
- "message"
- "debug"
Development/testing
test-mode: false
AI configuration
ai-provider: "openai" # Options: "openai" (default), "claude-code"
ai-model: "gpt-4"
Web dashboard (Dstl8 Lite)
web-port: 5718 # Port for the web dashboard
web-disabled: false # Set to true to disable
See examples/config.yml for a complete configuration example with detailed comments.
Gonzo supports multiple AI providers for intelligent log analysis. Configure using command line flags and environment variables. You can switch between available models at runtime using the m key.
```bash
→ →
 →
 →
 →
 →
 →
 →