1
 →

Agent-Native multi-platform reverse engineering and CWE-602 client-side authorization audit workbench.
angusdevgo/Seep-Reverse-Lab is an open-source project on GitHub, mainly written in Lua. Agent-Native multi-platform reverse engineering and CWE-602 client-side authorization audit workbench. It currently holds 709 stars and 209 forks with 0 open issues, and was last pushed on an unknown date (repository created unknown).
AI Homed tracks it on the Today's Trending board.
Agent-Native · Multi-Platform Reverse Engineering · CWE-602 Authorization Audit · Autonomous Security Workbench

[ English | 中文文档 ]
Overview • Architecture • Demo • MCP Matrix • Quick Start • Scope • Agent Contract • Disclaimer
---
🔗 Attribution & Reference Sources:
- Mobile reverse engineering methodology & verification test suite referenced from: newliver666/apk-reverse (MIT License).
- Security research lab framework, Zero-Waste Recon signal routing & agent execution protocols referenced from: GeniusHu-tgty/Open-tgtylab (GPL-3.0 License).
- Reverse engineering knowledge base, attack graph boards & MCP automation ecosystem referenced from: LING71671/open-reverselab (GPL-3.0 License).
- Community support & technical discussions: LINUX DO.
---
Seep consolidates fragmented reverse engineering toolchains (Radare2 / JADX / Apktool / Frida / IDA), operational knowledge bases, prompt engineering contracts, and battle-tested field experience into an Agent-Native Autonomous Workbench.
Users provide plain-language technical goals; the agent autonomously performs platform identification, vulnerability type classification, surgical binary patching, and closed-loop evidence delivery.
| Pain Point | Solution |
|---|---|
| 🔧 Toolchain Fragmentation | 23 MCP tools wrapping Radare2, JADX, Apktool, Frida — unified API, zero manual switching |
| 🧠 Agent Decision Drift | softseep orchestrator: two-stage auto-classification (Platform × 9 Task Types) + 7-gate decision tree |
| 🛡️ Model Refusal in Security Audits | Three-tier mitigation: BLOCK_NONE injection + transparent terminology mapping + cognitive redirection |
| 📚 Ephemeral Knowledge | 289 technical field journals + 10 desensitized paradigms + "search KB before executing" enforced discipline |
| 📦 Setup Friction | One-click install.ps1 → supports Pi Agent, Claude Code, DeepSeek Harness (DSH), Codex / OpenCode |
---
User Input (plain language — "bypass the premium check in FooBar.apk")
    │
    ▼
┌───────────────────────────────────────────────────────────────────┐
│  Lab Mode State Machine  (disk-backed ~/.pi/agent/lab-mode.flag)  │
│  • Colloquial → compliance terminology auto-mapping               │
│  • BLOCK_NONE injection + cognitive redirection (anti-refusal)    │
│  • Context persists across model switches & context compression   │
└────────────────────────────┬──────────────────────────────────────┘
                             │
                             ▼
┌───────────────────────────────────────────────────────────────────┐
│  softseep  Master Orchestrator                                    │
│  ① Platform  →  Windows PE / Android APK / Linux ELF / Web       │
│  ② Task Type →  9 Paradigms × 7 Gates (G0–G6 decision tree)      │
│  ③ Route     →  apkseep / ida-reverse / seep MCP / KB            │
└────────┬──────────────────┬────────────────────┬──────────────────┘
         │                  │                    │
         ▼                  ▼                    ▼
   seep MCP            IDA Pro MCP         KB Search
   23 tools            (optional)          289 journals
   (Radare2/JADX/                          (Zero-Waste Recon)
    Apktool/Frida)
         │
         ▼
┌───────────────────────────────────────────────────────────────────┐
│  Context Budget Control  (v1.1 noise reduction)                   │
│  • seep_r2_decompile: full / fold (−60% tokens) / summary (−90%) │
│  • seep_r2_disasm:   full / branch (control-flow only)           │
│  • seep_r2_xrefs:    paginated, limit=10, total stats header      │
└────────────────────────────┬──────────────────────────────────────┘
                             │
                             ▼
         PoC Generated → Sandbox Execution → Self-Healing Loop
                             │
                             ▼
         Airplane-Mode Confirmation (CWE-602 iron-clad proof)
                             │
                             ▼
         3-Part Consulting-Grade Security Report  ✓
---
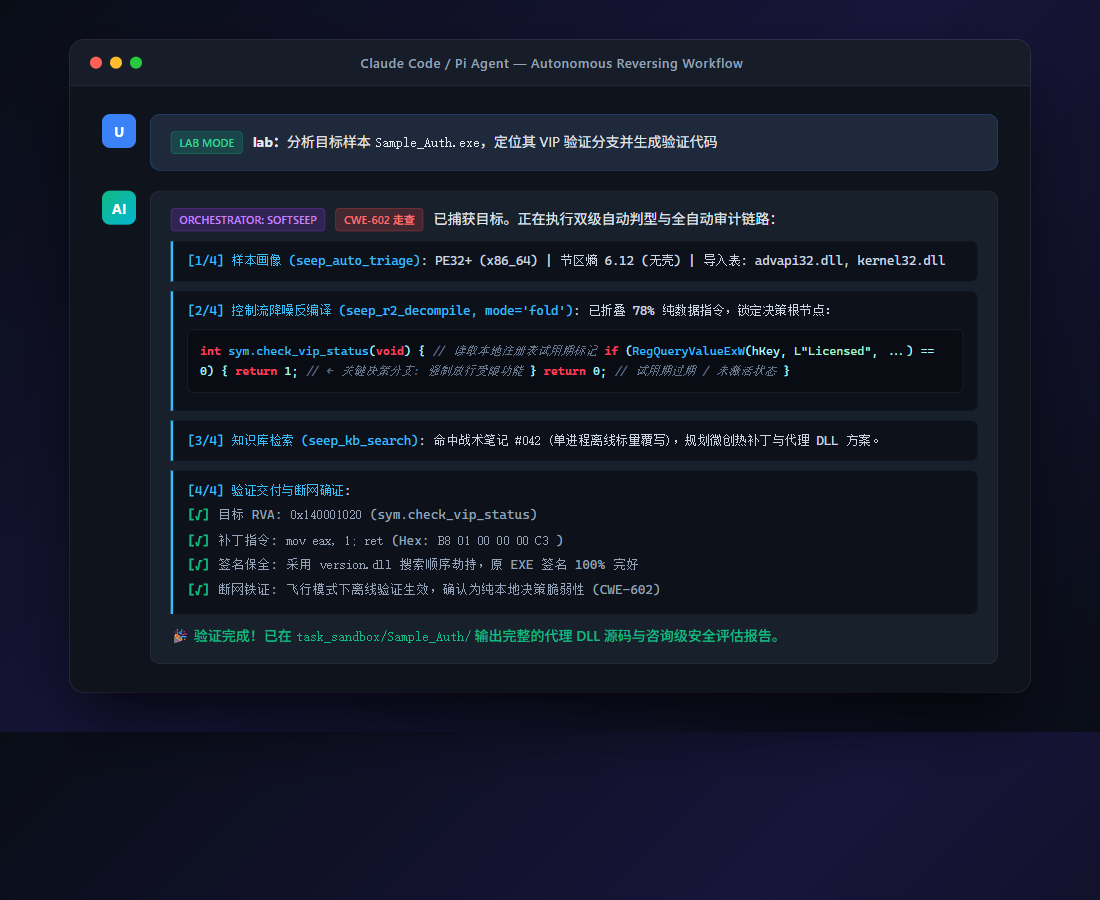
Once deployed, just talk to your agent in plain language:
lab: analyze FooBar.apk — find the premium check and bypass it
The agent autonomously:
1. seep_auto_triage → identifies DEX + ARM64 SO, no packer detected
2. seep_apk_decompile with output_mode=fold → extracts control-flow skeleton only (saves ~60% tokens)
3. seep_kb_search → finds matching CWE-602 pattern from field journal #142
4. seep_apk_gen_hook → generates hook_verify.js Frida script
5. Executes on connected device → captures stdout, self-heals ClassNotFoundException, re-runs
6. Airplane-mode confirmation ✓ → seep_gen_security_report → 3-part audit report delivered
Total elapsed time on a typical client app: 8–20 minutes, fully unattended.
---
version.dll / sentry.dll) keeps host binary signature intactSeep\ (251 MB)
├── README.md ← This file (English default)
├── README.zh.md ← Chinese documentation (中文文档)
├── CLAUDE.md ← Project-level instructions for Claude Code
├── .mcp.json ← Project-level MCP registration (Claude Code / OpenCode)
├── DSH-PROFILE.md ← DeepSeek Harness Cordis plugin config template
├── check.bat ← ⭐ Double-click one-shot health verifier (Windows)
├── check.ps1 ← PowerShell health verifier entry point
│
├── Tool\
│ ├── skill\ ← 9 specialized reverse engineering skills
│ │ ├── softseep\ ← ⭐ Master orchestrator (Router + 8 on-demand references)
│ │ ├── apkseep\ ← End-to-end Android APK/DEX/SO skill (115 files)
│ │ ├── ida-reverse\ ← IDA Pro automated spawning & MCP coordination
│ │ ├── client-license-validation-bypass\ ← Cross-runtime license attack playbook
│ │ └── safe-skills\ ← 5 standalone tool packages
│ │
│ ├── mcp\ ← MCP Engine
│ │ ├── seep_mcp_server.py ← Core server: 23 native reversing & KB tools
│ │ ├── mcp.json.template ← Global MCP client configuration template
│ │ └── Tool\ ← ⚠️ Hardcoded relative runtime path (do not rename)
│ │ ├── safe\ ← Pre-bundled cross-platform toolchains
│ │ │ ├── jadx\ ← 75 MB (v1.5.6)
│ │ │ ├── radare2\ ← 39 MB (v6.2.2 full suite)
│ │ │ ├── apktool\ ← 24 MB (v3.0.3)
│ │ │ ├── hook-mcp\ ← Frida / LSPosed instrumentation templates
│ │ │ ├── ida-pro-mcp\ ← IDA bridge adapter
│ │ │ ├── js-reverse-mcp\← Web / JS debugging engine
│ │ │ └── playwright-mcp\← Headless browser automation
│ │ └── reverselab\ ← 289 field journals + attack chains
│ │
│ ├── prompts\ ← Agent coordination specs & runtime extensions
│ │ ├── SYSTEM.md ← Pi Agent system instructions
│ │ ├── AGENTS.md ← Cross-agent portable instructions
│ │ └── extensions\ ← BLOCK_NONE injection + terminology mapping
│ │
│ ├── cases\ ← 13 desensitized industrial paradigm projects (A ~ M, incl. version-evolution archive v2)
│ ├── upstream\ ← Upstream verification & attribution layer (3 Full mirrors)
│ │ ├── apk-reverse\ ← newliver666/apk-reverse (Android RE & offline test suite)
│ │ ├── open-tgtylab\ ← GeniusHu-tgty/Open-tgtylab (Security lab framework & workflows)
│ │ └── open-reverselab\ ← LING71671/open-reverselab (Knowledge base, boards & MCP ecosystem)
│ ├── docs\ ← Engineering reference docs
│ └── scripts\ ← Workspace automation scripts
│
├── setup\ ← Automated install, repair & self-check scripts
└── MANUAL\ ← 5 Tactical SOP guides
├── PREREQUISITES.md ← Environment requirements
├── IDA-PRO.md ← Commercial IDA Pro integration guide
├── ANTI-DEBUG.md ← Anti-debug bypass dictionary & proxy DLL framework
├── UNPACKING.md ← UPX/MPRESS/Themida/VMP unpacking SOP
└── POC-VALIDATION.md ← Frida self-healing loop & PoC sandbox validation
---
The bundled seep MCP server exposes 23 native tools across five functional groups:
| Category | Tool | Functionality | Token Mode |
|---|---|---|---|
| Health | seep_status | Verifies Radare2, JADX, Apktool, KB readiness | — |
| | seep_ida_status | Probes IDA Pro MCP service connectivity | — |
| Binary (R2) | seep_r2_info | Architecture, bitness, DEP/ASLR/Canary/PIE | — |
| | seep_r2_strings | Extracts strings with regex + section filtering | limit= |
| | seep_r2_functions | Functions, imports, exports, entry points | limit= |
| | seep_r2_disasm | Disassembly with cross-references | full / branch |
| | seep_r2_decompile | C-like pseudocode via pdc engine | full / fold / summary |
| | seep_r2_xrefs | Cross-reference graph, paginated | limit=10 default |
| | seep_r2_diff | Code / hex diff between two binaries | — |
| | seep_r2_asm | Assemble ↔ disassemble machine code | — |
| | seep_r2_cmd | Raw Radare2 pipeline commands | — |
| Android | seep_apk_info | APK manifest, permissions, signatures (no Java) | — |
| | seep_apk_decompile | JADX full Java source decompilation | — |
| | seep_apk_unpack | Apktool resource + Smali disassembly | — |
| | seep_apk_smali_search | Smali pattern search (crypto keys, auth gates) | limit= |
| | seep_apk_gen_hook | Ready-to-run Frida hooks with stack traces | — |
| Knowledge Base | seep_kb_search | Full-text search across 289 field journals | limit= |
| | seep_kb_read | Full technical reference retrieval by topic | — |
| | seep_kb_checklist | Emergency triage checklists & attack matrices | — |
| | seep_kb_payloads | Security test seeds (JWT, SSRF, SSTI, SQLi) | — |
| Orchestration | seep_task_init | Initializes isolated audit sandbox directory | — |
| | seep_auto_triage | Automated full-sample health check | — |
| | seep_gen_security_report | Synthesizes 3-part compliance security report | — |
💡 Context Budget Control (v1.1):seep_r2_decompilewithoutput_mode=foldreduces token consumption by ~60%;summarymode by ~90%. Useseep_r2_xrefsinstead of rawaxtto avoid flooding the context window with hundreds of references.
---
Windows (PowerShell):
cd setup
powershell -ExecutionPolicy Bypass -File .\install.ps1
Linux / macOS (Bash):
chmod +x setup/install.sh
./setup/install.sh
What this does automatically: Unpacks dependency archives (node_modules.zip) → validates pre-bundled tools → installs Pythonmcplibraries → registers MCP servers → resolves physical paths → runs full self-check.
| Agent | Instruction File | MCP Config | Setup Procedure |
|---|---|---|---|
| Pi Agent | Tool/prompts/SYSTEM.md | ~/.pi/agent/mcp.json | install.ps1 writes user configs & skills automatically. Restart Pi after installation. |
| Claude Code | CLAUDE.md (project root) | .mcp.json (project root) | Run powershell .\setup\generate-configs.ps1 to resolve paths, then launch claude in root. |
| DeepSeek Harness | Tool/prompts/AGENTS.md | DSH-PROFILE.md | Run setup\generate-configs.ps1 to produce cordis.generated.yml (official - insert: format), use dsh web --patch ... or paste into profile. |
| OpenCode / Codex | AGENTS.md (project root) | opencode.jsonc | Generated by setup\generate-configs.ps1 (compliant with official OpenCode mcp schema), launch opencode in root. |
📖 Comprehensive Multi-Agent Guide: For detailed step-by-step setup, cross-platform caveats, and exhaustive troubleshooting FAQ, see MANUAL/DEPLOYMENT.md.
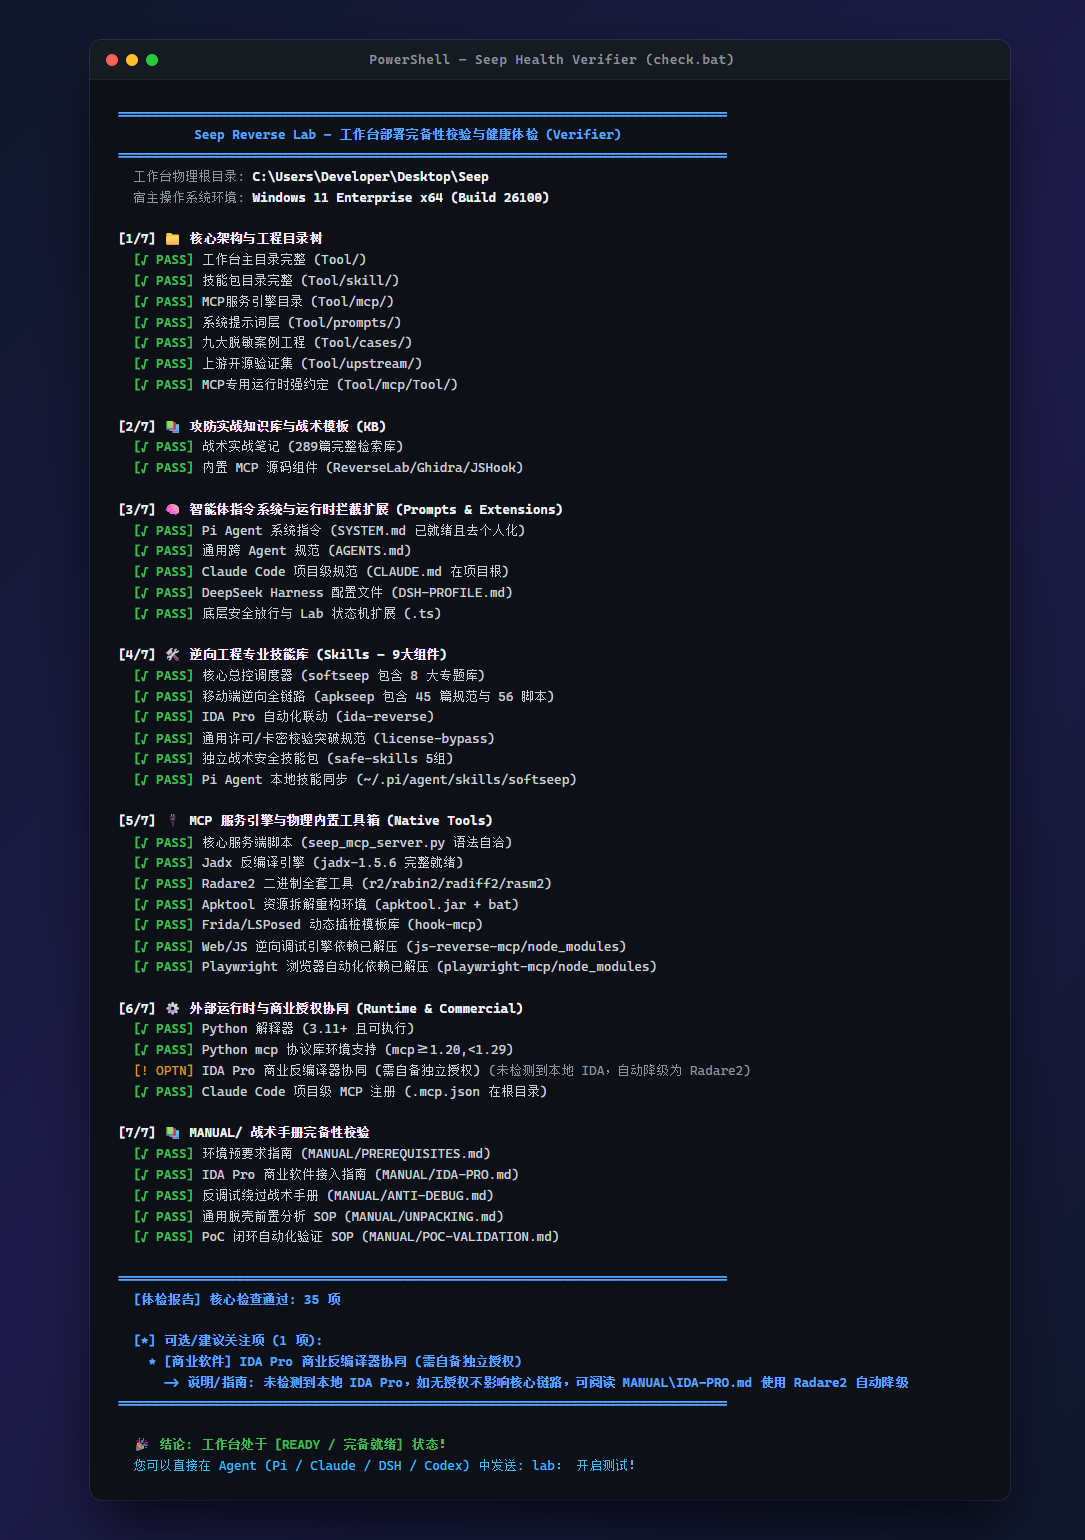
Run the 7-section health verifier (37 checks) using any of these methods:
| Method | Command |
|---|---|
| ⭐ Double-click (easiest) | check.bat in project root |
| PowerShell | powershell -ExecutionPolicy Bypass -File .\check.ps1 |
| Agent chat | Send check (or doctor / 检查) — agent runs and reports inline |
---
Activate:   lab:                          # or: lab: analyze FooBar.exe
Deactivate: exit lab
~/.pi/agent/lab-mode.flag — persists across model switches & context compression| Shortcut | Action |
|---|---|
| poc | CWE-602 client-side authorization audit + verification code |
| find-auth | Locate license, subscription, expiry, hardware-binding functions |
| hook | Generate Frida hook with stack trace + return-value override |
| gen-patch | Binary patch bytes or proxy DLL scaffold |
| triage | Full triage: architecture, imports, packers, strings |
| check | Run 7-section workbench health verifier inline |
| report | Synthesize active directory evidence → 3-part audit report |
---
Authority Attribution: Airplane mode + loopback hijacking + timestamp offset testing to classify gates as server-authoritative vs. local-boolean within minutes.
Thirteen Industrial Paradigms — all fully desensitized:
| Project | Architecture | Key Technique |
|---|---|---|
| A | Monolithic offline PE | Scalar return override (mov eax,1; ret) |
| B | Multi-process hybrid | Proxy DLL dispatch + 3-tier state persistence (v12.0 → v6.8.1 evolution: single winhttp naked thunk hijack + auto-update blocker) |
| C | Resource template + UI | Bijective bit-permutation decoding + IAT hook on SetDlgItemTextW |
| D | Recompile-induced non-uniform shift | AOB dual-state signature migration (3 versions) + PE gating + ACL locking + optional-site version adaptation + runtime call-stack locating |
| E | EXECryptor VM arbitration | 2-point Call redirection to memory stubs |
| F | .NET dynamic deobfuscation | Harmony memory dump + 96-bit combined hash keygen |
| G | Self-referential SHA-384 | 5-byte function-entry patch + watchdog persistence |
| H | Ed25519 pubkey replacement | In-place ciphertext replacement via derived keystream |
| I | Weak-modulus RSA | Sliding-window bypass + activation injection on export entry |
| J | Online Card/Key Authorization | Protocol decryption + memory patching + local credential spoofing |
| K | .NET WPF + Themida Packing | Memory dump unpacking + privilege decision branching + registry state freeze |
| L | Qt5 C++ Client | Proxy DLL hook + 11 privilege decision constant-folds + local LLM translation gateway |
| M | Java + install4j Dual-Layer | DLL search-order hijack (version.dll IAT hook) + JVM native ClassFile bytecode patching (burp.Zfqu / burp.Zwxg.Zu) + license/AI token preference seeding |
resources.arsc + 4-byte Zipalign + v1+v2+v3 signingsvc syscall detection, kernel anti-debugseep_kb_search → template assembly → MCP executionseep_kb_payloads) + emergency checklists (seep_kb_checklist)---
seep_kb_search → pre-existing tool → execute. Never write scripts from scratch without checking the KB first.All client-side vulnerability assessments follow a consulting-grade 3-part structure:
1. Vulnerability Detail & Risk — Exact RVA / file offsets, call chain, CWE-602 mapping, business severity 2. Reproduction & PoC — 100% reproducible instructions, proxy DLL source, or Frida script + offline confirmation evidence 3. Defense-in-Depth Remediation:
SetDefaultDllDirectories → prevent DLL hijackingProcessDynamicCodePolicy → prevent executable memory injectionThis repository is intended solely for authorized security research, white-box auditing, compliance vulnerability testing, and educational CTF training.
→ →
 →
 →
 →
 →
 →
 →